
 Repository
Current collected state Current
Observed since 20 Oct, 16:47 UTC
No superseded metadata states collected. Unchanged observations do not create new revisions.
Flags characters that are on an ESI ACL but not registered in Alliance Auth
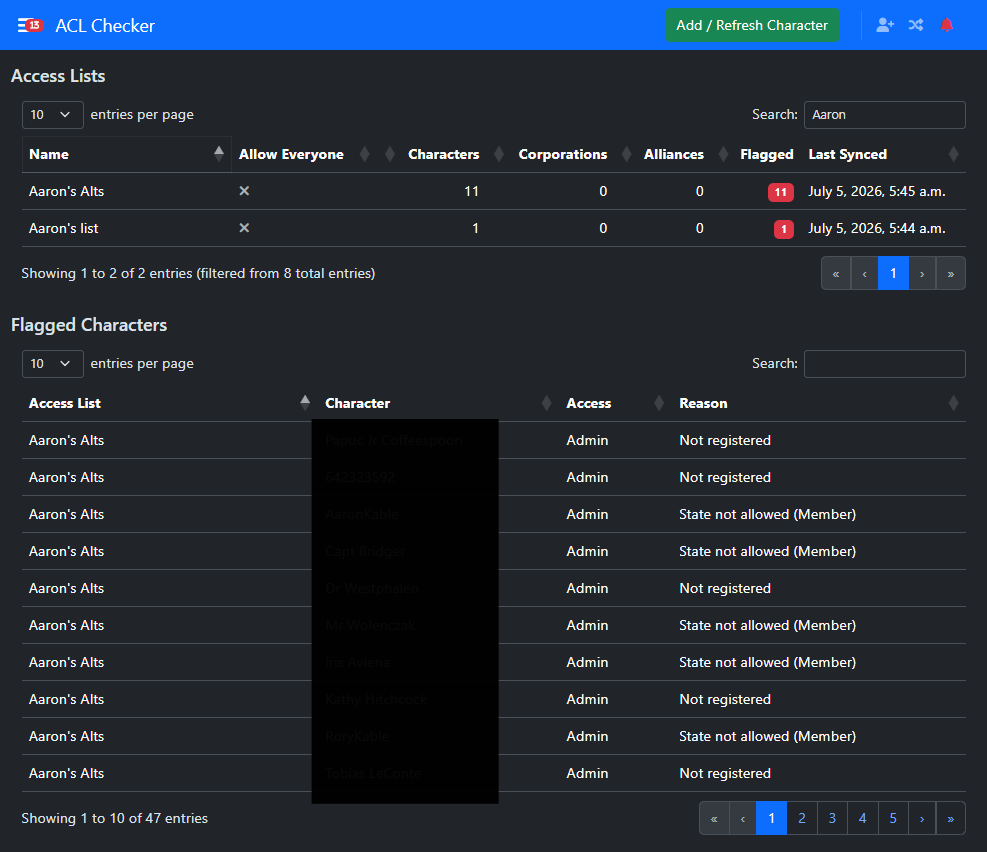
A plugin app for Alliance Auth (AA) that pulls Access Control Lists (ACLs) from EVE's ESI API, stores them in the database, and flags characters that appear on an ACL but are not registered in Auth.


[!IMPORTANT]
This app needs Alliance Auth v5!
Make sure you're in your venv, then install it in editable mode:
pip install -e aa-acl-checker
Add acl_checker to INSTALLED_APPS in settings/local.py, then run:
python manage.py makemigrations
python manage.py check
python manage.py migrate
Finally, restart your AA server.
pip install git+https://github.com/Solar-Helix-Independent-Transport/aa-acl-checker
Then add acl_checker to INSTALLED_APPS in settings/local.py, run migrations and
restart your allianceserver.
add_owner permission clicks "Add /
Refresh Character" and authorizes with the esi-access.read_lists.v1 scope.
ESI only lets a character list Access Lists it is a Manager or Admin of, so
the linked character must actually hold one of those roles on the ACLs you
want tracked. Linking immediately queues a sync and re-authorizes an
already-linked character if its token has expired or lost the scope.Allowed/Manager/Admin on a tracked ACL but who has no
linked, owned character in Auth - i.e. someone with structure/fleet access
who was never (or is no longer) registered.Linking a character syncs its Access Lists once immediately, but nothing refreshes them after that unless a periodic task is scheduled. Run this once after installing/upgrading:
python manage.py acl_checker_setup
This registers an hourly PeriodicTask (via django-celery-beat) that calls
acl_checker.tasks.update_all_acls for every tracked (active) owner
character. It's safe to run again after upgrades - it just updates the
existing schedule rather than duplicating it.
For each active Owner (a character with a valid esi-access.read_lists.v1
token):
GET /characters/{character_id}/access-lists lists the Access Lists that
character manages or administers.GET /characters/{character_id}/access-lists/{access_list_id}
fetches its full membership - separate lists of characters, corporations,
and alliances, each with an access level (Unspecified/Allowed/Blocked/
Manager/Admin).ESI never includes a name alongside a character/corporation/alliance ID in
the Access List detail, so none is cached locally - display names are
resolved from Auth's own EveCharacter cache at read time instead.
Flagging is computed live, not stored: AclCharacterEntry.objects.flagged()
checks whether a granted character_id has an owned EveCharacter in Auth.
That means a character clears the flagged list the moment someone registers
it, and a newly-added ACL character shows up as flagged immediately on the
next sync - no separate reconciliation step required.
Write your unit tests in acl_checker/tests/ using the test_ filename prefix.
Download counts and popularity will appear here as the collector receives them.
| Version | Published | Direct dependencies | Open version |
|---|---|---|---|
| 0.0.1 | 5 Jul 2026 | 3 |
This describes our collected data; it is not a security assessment.
Shared repository data · GitHub
Observed since 20 Oct, 16:47 UTC
No superseded metadata states collected. Unchanged observations do not create new revisions.
package:ad4a182998e85b1ae5e2135464fc716e11728e67d521d1579a05268ba9415fde