
 Repository
Current collected state Current
Observed since 20 Oct, 19:52 UTC
No superseded metadata states collected. Unchanged observations do not create new revisions.
Free Active Directory pentesting CLI for AD enumeration, attack paths, Kerberoasting, AS-REP roasting, ADCS, DCSync, password spraying, and CTF labs.


Free Active Directory pentesting tool. Replace your AD pentest toolchain with one CLI.
ADscan is a free CLI for pentesters, red teamers, and security consultants. It covers 107 Active Directory attack techniques in a single workflow: enumeration, Kerberoasting, AS-REP roasting, ADCS/ESC exploitation, DCSync, credential harvesting, and native attack-path analysis. It runs on Linux and macOS through Docker, and natively on Windows as a self-contained bundle with no Docker and no Python install.

Real run, no cuts: ADscan takes HTB Forest from zero access to Domain Admin in ~3 minutes, unattended.
On Linux or macOS, ADscan runs inside Docker, so you need Docker Engine installed and running, and about 12 GB of free disk for the runtime image (the installer requires 15 GB free before it will pull).
docker version   # if this fails, install Docker first
pipx install adscan
adscan install
adscan start
On Windows, there is no Docker and no Python to install: download the self-contained ADscan bundle and run adscan.exe directly. The bundle carries its own runtime and tools, so it works on a hardened, locked-down host — the common assumed-breach scope where you only have a domain-joined Windows box.
Docker install steps per distribution, the Windows bundle download, and everything else: adscanpro.com/docs
Once inside the shell, start an unauthenticated recon:
(ADscan) > start_unauth
This discovers domain controllers, SMB exposure, null sessions, and roastable accounts without credentials. From there, run start_auth with a domain user to enumerate LDAP, collect BloodHound data, and build the attack graph.
adscan ci runs the whole pipeline non-interactively: preflight, recon, enumeration, exploitation, reporting, no prompts. Same engine, no shell. It is a PRO capability — automation and unattended runs are what you're paying for; the free LITE tier gives you the full interactive adscan start shell on every platform.
# Authenticated scan of a domain
adscan ci auth --type audit --interface eth0 \
  --domain corp.local --dc-ip 10.0.0.1 -u alice -p 'S3cr3t!'

# Unauthenticated sweep
adscan ci unauth --type audit --interface eth0 --dc-ip 10.0.0.1
--type, --interface and the auth/unauth positional are required. adscan ci --help lists the rest.
adscan ci makes every decision the interactive shell would ask you about, so it's built for pipelines, lab automation, and unattended engagement runs. For client work where you want to review each decision, the interactive adscan start shell (free on LITE) is the supported path.
Most AD pentesters use 5-8 separate tools. ADscan replaces the chain:
| ADscan | NetExec/CrackMapExec | Certipy | Impacket | BloodHound CE | |
|---|---|---|---|---|---|
| Platform | Linux/Win | Linux/Win | Linux | Linux | Linux/Win |
| AD enumeration | Full | Partial | No | Partial | No |
| Kerberoasting | Yes | Yes | No | Yes | No |
| ADCS ESC1-16 | Yes (auto) | No | Yes (manual) | No | No |
| Attack paths | Native graph | No | No | No | Yes |
| DCSync | Yes | Yes | No | Yes | No |
| Single workflow | Yes | No | No | No | No |
| Compliance reports | PRO tier | No | No | No | No |
ADscan is not a replacement for every tool in every scenario. It is the fastest path from credentials to a documented attack chain in a single terminal session.
ADscan covers 107 Active Directory attack techniques across the kill chain — see the full technique coverage table, generated from the product catalog and mapped to MITRE ATT&CK:
LITE (Free, Source Available)Everything a pentester could do manually, without the toolchain:
|
PROWhat takes days manually, automated:
|
Unauthenticated recon:
adscan start
# Inside the ADscan shell:
start_unauth
Discovers domain controllers, DNS, SMB null sessions, and roastable accounts without credentials.
Authenticated scan with BloodHound collection:
# Inside the ADscan shell (after start_auth):
start_auth
Collects LDAP data, builds the attack graph, and identifies Kerberoasting targets, ADCS misconfigurations, and privilege escalation paths.
More walkthroughs:
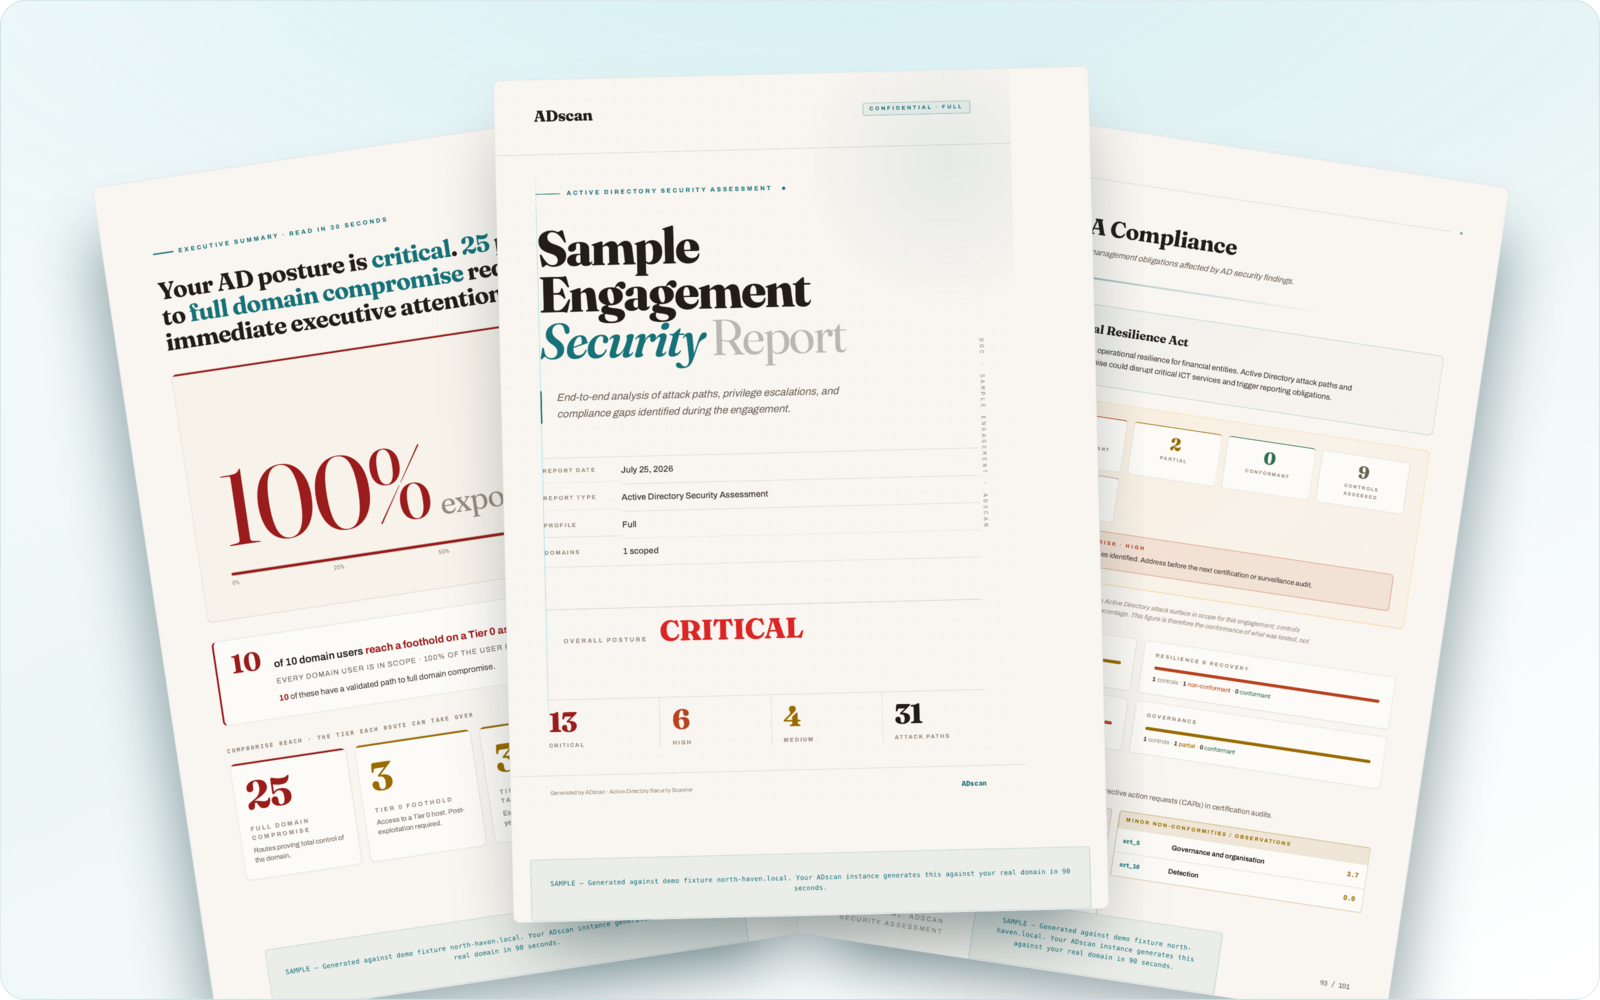
The PRO deliverable is an audit-ready PDF an executive and a sysadmin can both act on: a posture score, attack-path analysis, and per-framework compliance mapping. The pages above come from a sample engagement against a lab domain.
ADscan LITE gives you enumeration, attack paths, and findings in the terminal. ADscan PRO turns them into three client-ready PDFs in 90 seconds:
Beta access is free for security consultants. adscanpro.com/pro
| OS | Linux (Debian/Ubuntu/Kali/Parrot) or macOS with Docker Desktop; or Windows via the native self-contained bundle (no Docker, no Python) |
| Docker | Required on Linux/macOS (Docker Engine; Compose is no longer needed). Not used by the Windows bundle |
| Disk | Linux/macOS: 15 GB free before install, runtime image roughly 12 GB unpacked. Windows bundle: a few hundred MB |
| Privileges | Linux/macOS: docker group or sudo. Windows: runs as a normal domain user, no local admin required |
| Network | Internet to pull the image or download the bundle, plus the target network |
Does ADscan work without a Windows machine? Yes. On Linux (or macOS) ADscan runs entirely inside Docker. No Windows VM, no RDP, no agent installation required. It connects to your target AD environment over the network using standard protocols (LDAP, SMB, Kerberos).
Does ADscan run natively on Windows?
Yes. There is a self-contained Windows bundle that runs adscan.exe directly — no Docker, no Python install, no local admin. It carries its own runtime and tools, so it works on a hardened, locked-down host, which is the usual assumed-breach scope where your only foothold is a domain-joined Windows box. The same engine runs on both platforms; only the packaging differs. On Windows without a GPU, password cracking falls back to CPU automatically, and the port scan runs in-process (no Npcap driver needed).
Is ADscan safe to run in production Active Directory environments? ADscan LITE is read-only by default for enumeration. Exploitation steps (Kerberoasting, credential dumping, DCSync) require explicit operator confirmation. Run it in a test window with your client's written authorization. See the security policy for responsible use guidelines.
How is ADscan different from BloodHound? BloodHound is a graph analysis tool that requires separate data collection (SharpHound or AzureHound). ADscan collects data, builds the attack graph, and executes the attack chain from one terminal. LITE includes native graph collection compatible with BloodHound CE. PRO adds algorithmic attack path auto-exploitation.
uv sync --extra dev
uv run adscan --help
uv run adscan version
Quality checks:
uv run ruff check adscan_core adscan_launcher adscan_internal
uv run pytest -m unit
Bug reports, lab reproductions, command-output samples, and focused pull requests are welcome. See CONTRIBUTING.md for the PR workflow and required checks.
Enterprise support: hello@adscanpro.com
Built by Yeray Martin Dominguez, a working AD pentester. I share a new Active Directory attack technique most weeks — follow along on LinkedIn or X.
Source available under the Business Source License 1.1.
(c) 2024-2026 Yeray Martin Dominguez | adscanpro.com
Download counts and popularity will appear here as the collector receives them.
| Version | Published | Direct dependencies | Open version |
|---|---|---|---|
| 13.2.0 | 10 Oct 2026 | 48 |
This describes our collected data; it is not a security assessment.
Observed since 20 Oct, 19:52 UTC
No superseded metadata states collected. Unchanged observations do not create new revisions.
package:563e7c4924dea7098b22500c70708e64b18eb1cac7384ee372cf4b08d48f3a72