
 Repository
Current collected state Current
Observed since 20 Oct, 21:33 UTC
No superseded metadata states collected. Unchanged observations do not create new revisions.
Open security scanner and self-hosted control plane for AI, MCP, and cloud infrastructure.
Open security scanner and self-hosted control plane for AI, MCP, and cloud infrastructure.
Find vulnerable software behind your AI agents—and trace the exposure evidence.
For AppSec and platform engineers: scan repositories and MCP configurations, inspect connected findings, and verify a changed dependency with a rescan. Credential references are names, not secret values. Recorded relationships do not prove exploitation or successful data access.
pip install agent-bom
agent-bom scan .
The scan prints inventory, findings, recorded exposure, evidence coverage, and
the next remediation step. Run agent-bom doctor if the first scan cannot
start.
For a deterministic sample, use the built-in offline demo. It deliberately
contains blocking findings, so status 1 is the expected security verdict;
the printed report is complete.
agent-bom scan --demo --offline
The demo uses a curated sample for reproducible output within a release; advisory and severity updates can change later releases.
If you want an inspectable sample before scanning your own repo:
agent-bom samples first-run
agent-bom scan --inventory agent-bom-first-run/inventory.json -p agent-bom-first-run --enrich
The bundled first-run stack includes agent inventory, MCP server definitions,
placeholder credential environment variable names, Python/npm manifests, and a
prompt file. See docs/FIRST_RUN.md in the repository for the guided flow.
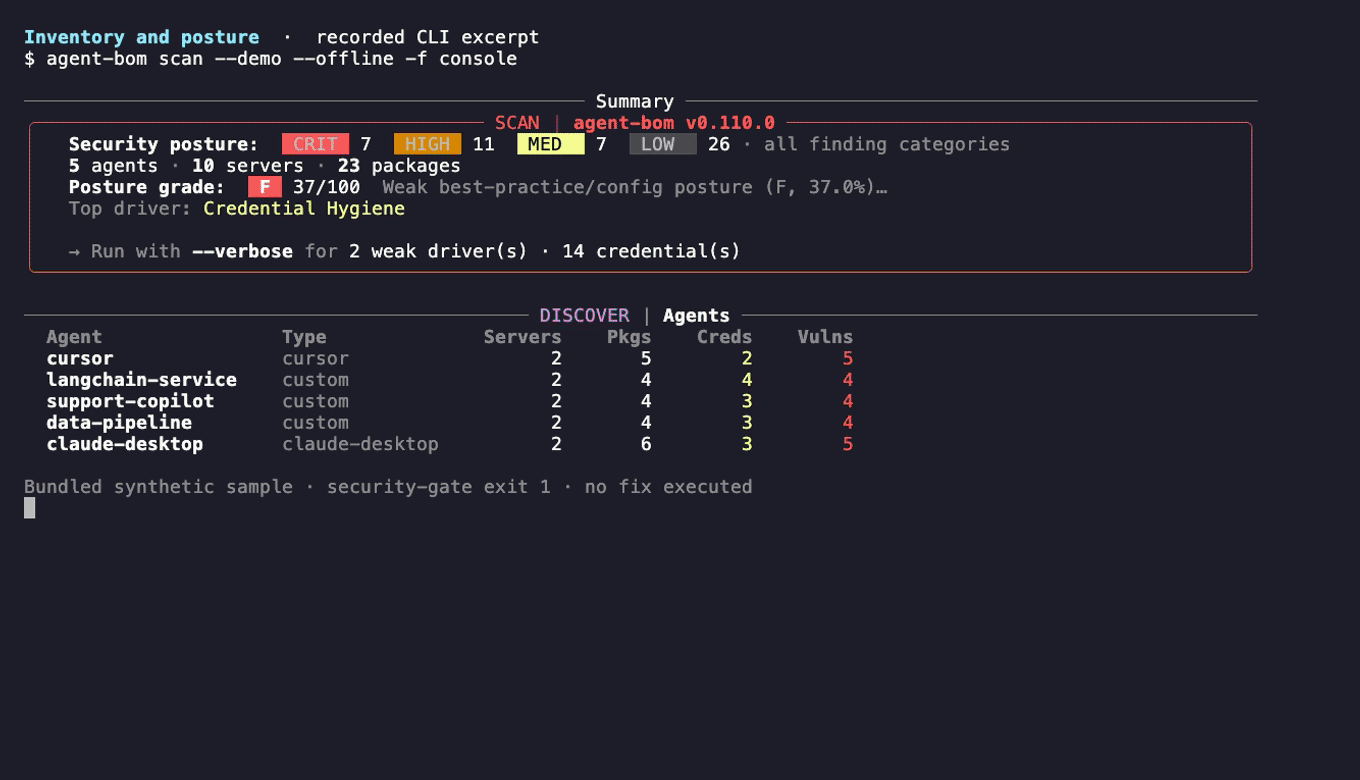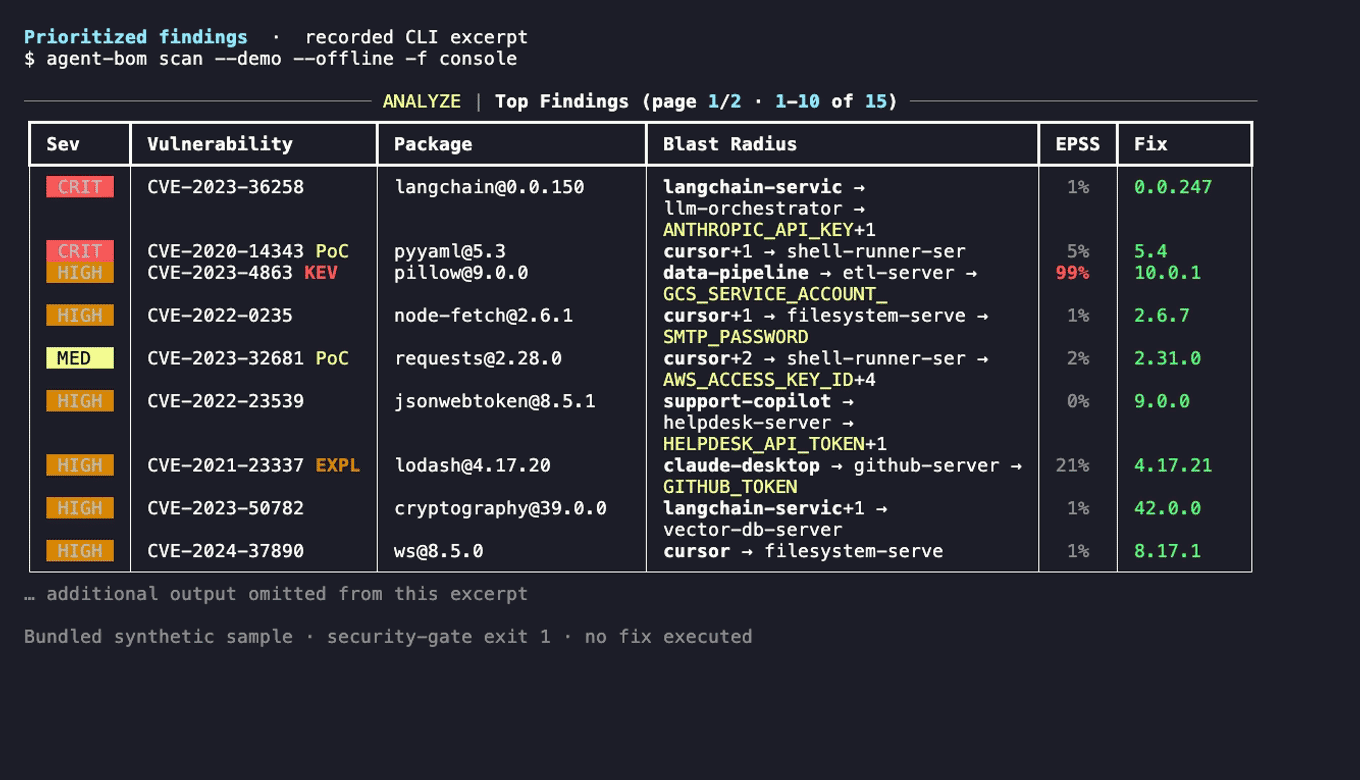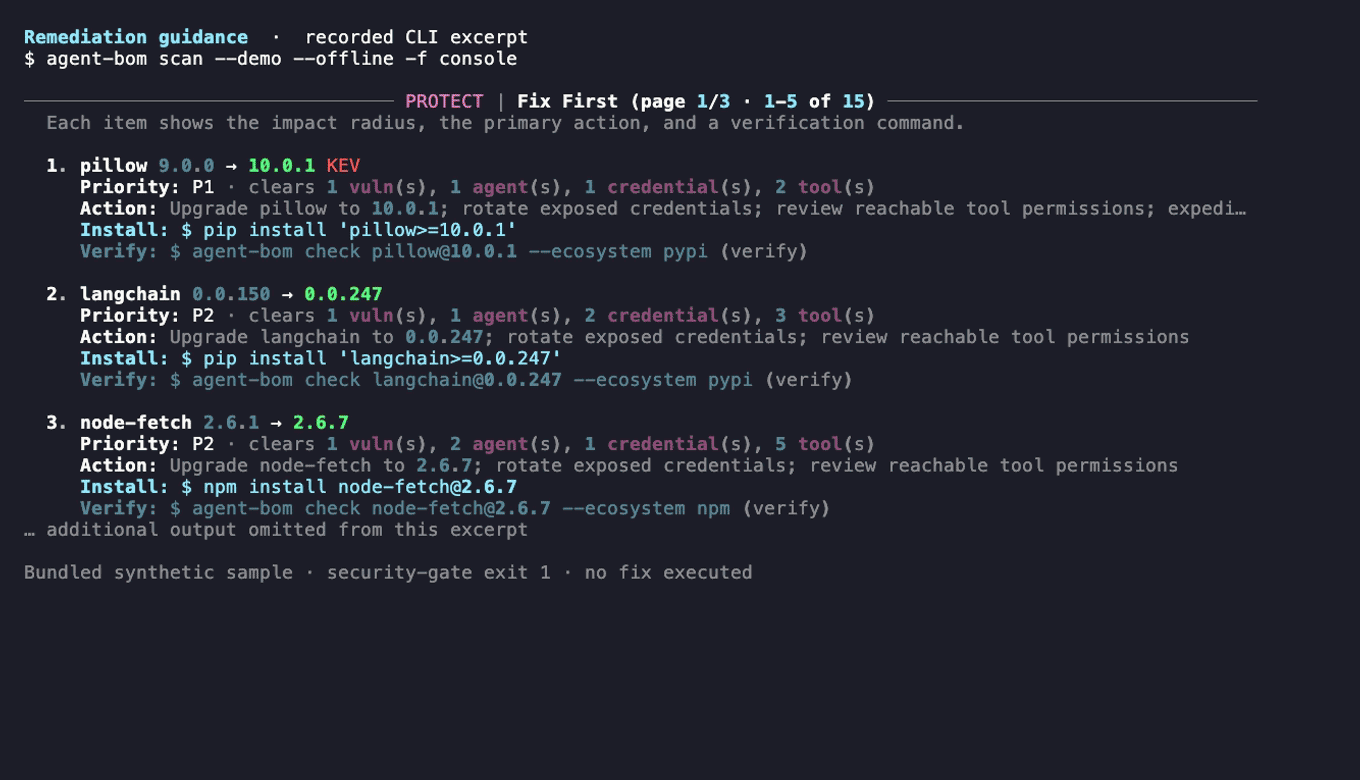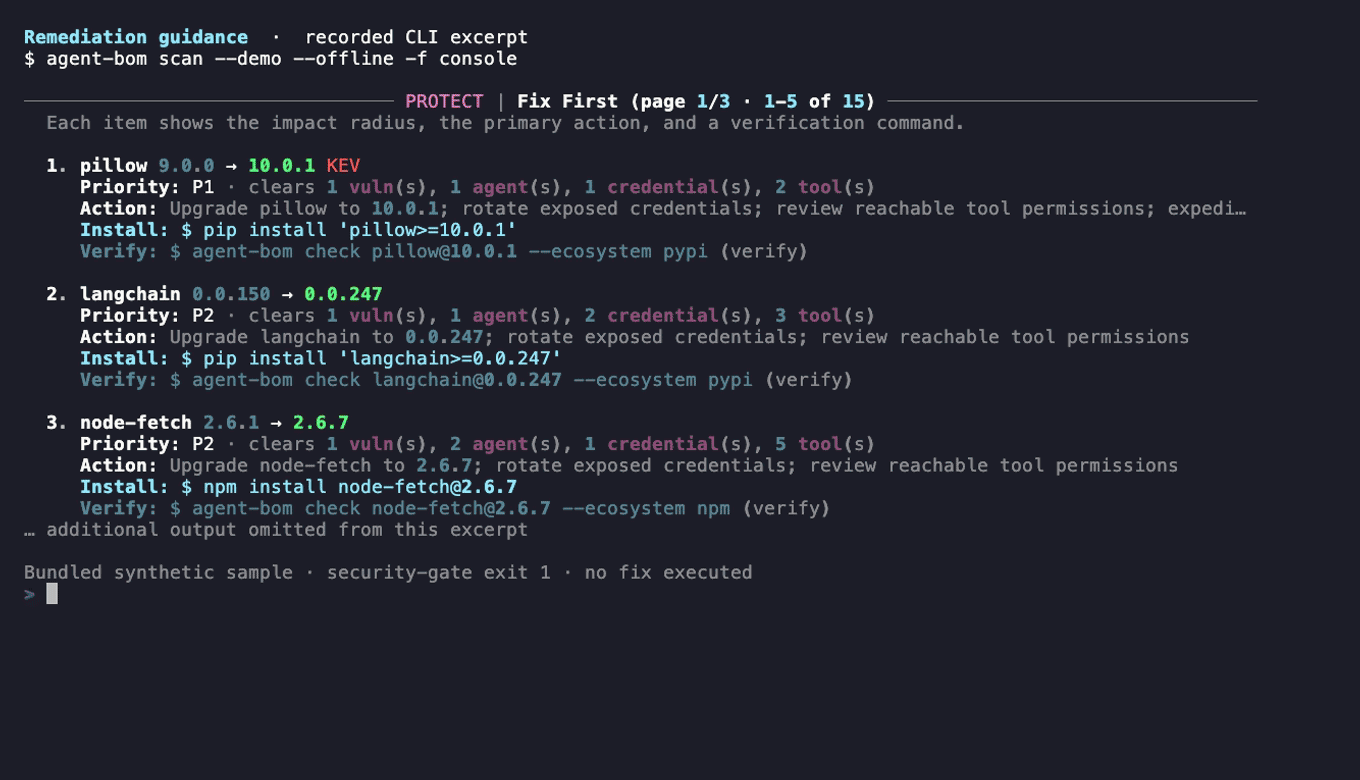
In the self-hosted dashboard, open Inventory → component → Findings → Compliance. The views retain the exact component and scan snapshot, expose recorded relationships and source evidence, and export loaded evidence with completeness receipts. Control mappings do not establish evaluated passes or certification.
From a source checkout, run the connected-BOM example. It retains before/after SQLite snapshots: a changed dependency input removes one pinned advisory finding while an unrelated synthetic cloud check remains failed. This bounded example does not change a deployment or qualify a cloud account.
pip install agent-bom

agent-bom scan .                                 # Repo + MCP + package blast radius
agent-bom quickstart --dry-run --offline          # Sample-data and API/UI next steps
agent-bom samples first-run                      # Inspectable sample AI stack
agent-bom check flask@2.2.0 --ecosystem pypi     # Pre-install package verdict
agent-bom image nginx:latest                     # Container image scan
agent-bom scan . --remediate remediation.md       # Fix-first remediation plan
pip install 'agent-bom[ui]'                      # once, if you want the dashboard
agent-bom serve --persist ~/.agent-bom/control-plane.db  # restart-safe local control plane
The base wheel is the scanner/CLI path and includes MCP server mode
(agent-bom mcp server). Install optional surfaces explicitly:
pip install 'agent-bom[ui]' for the local API/dashboard process. Use
pip install 'agent-bom[all]' for supported first-run extras; MLflow remains
separate until its upstream CVE backlog is fixed. If an extra is missing, the
command exits with the matching install hint.
Self-hosted pilot:
curl -fsSL https://raw.githubusercontent.com/koda-ai-studio/agent-bom/main/deploy/docker-compose.pilot.yml -o docker-compose.pilot.yml
docker compose -f docker-compose.pilot.yml up -d
# Dashboard -> http://localhost:3000
Production chart from a checked-out repo:
helm upgrade --install agent-bom deploy/helm/agent-bom \
  --namespace agent-bom --create-namespace \
  -f deploy/helm/agent-bom/examples/eks-production-values.yaml
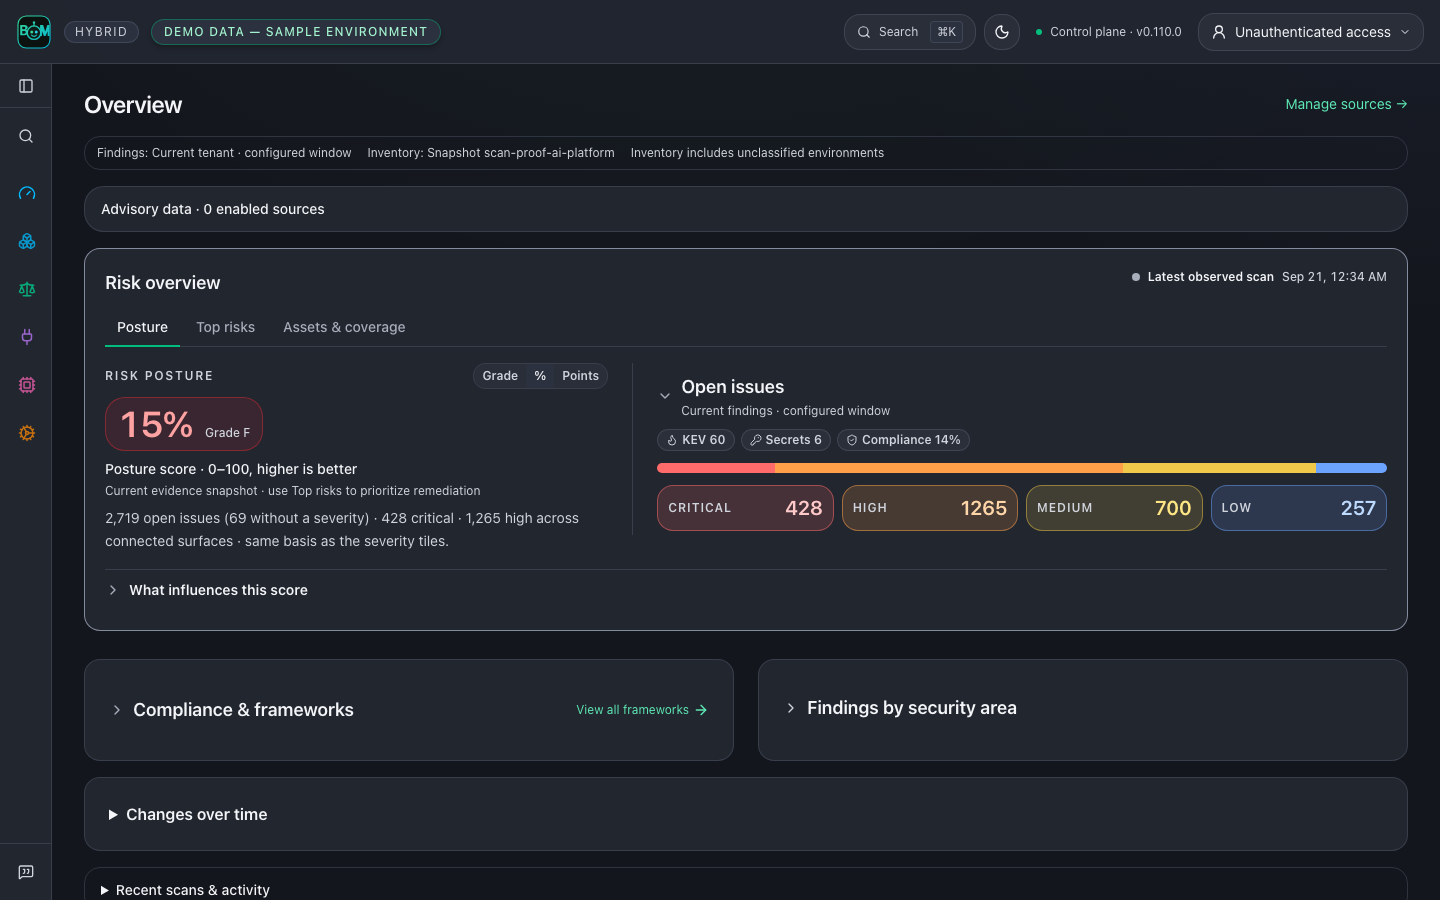
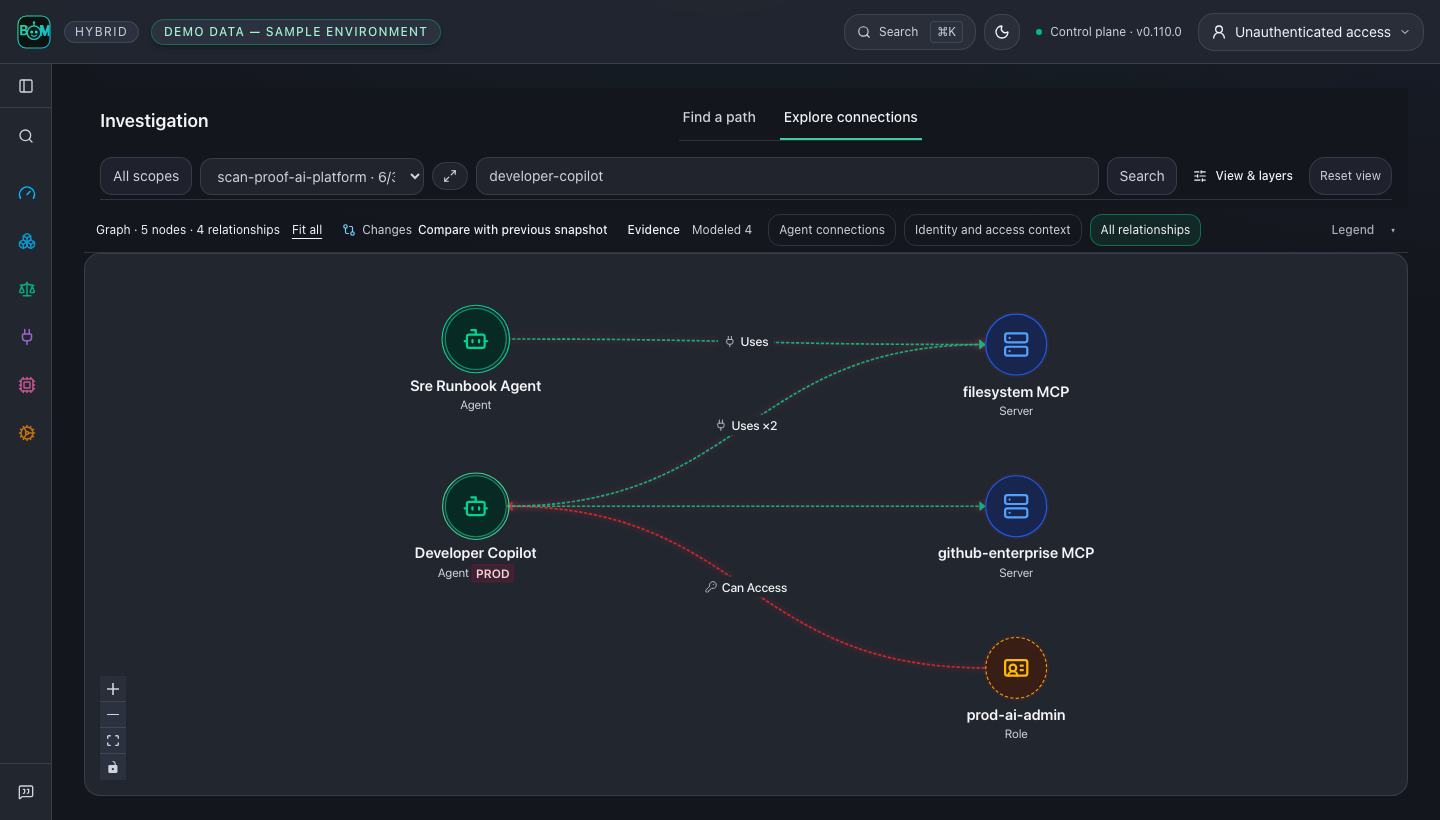
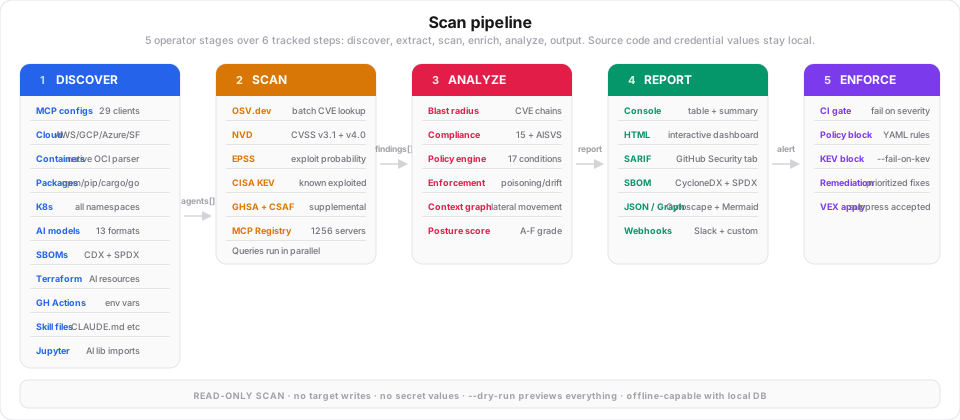
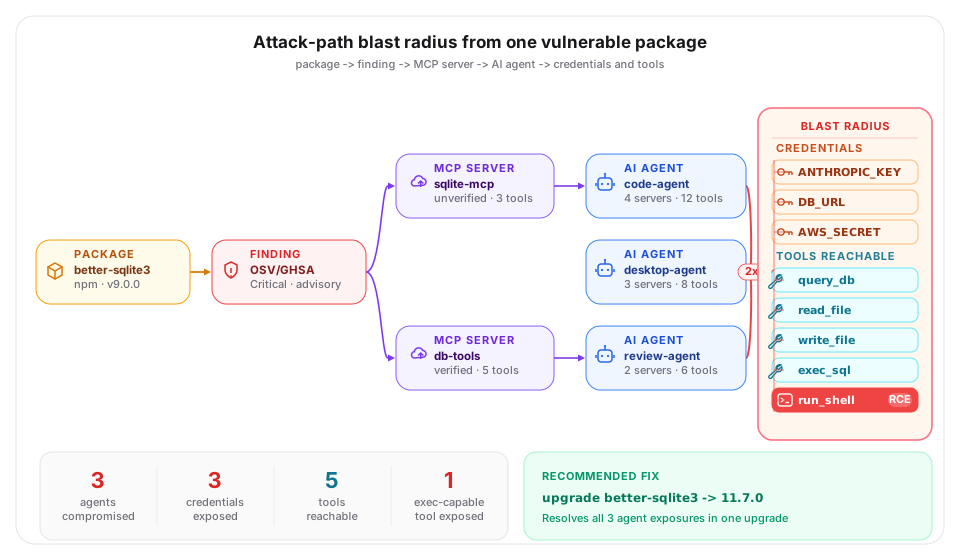
CLAUDE.md, AGENTS.md, .cursorrules, .windsurfrules, skills/*mix.lock / pubspec.lock for Hex and Pub) with OSV/GHSA enrichment and blast radiusUnifiedGraph, from package → finding → MCP server → credentials → connected agentsagent-bom mcp server --profile full for the complete catalog of 94 MCP tools, 7 resources, and 8 workflow prompts in Claude, Cursor, Windsurf, and Cortex CoCo / Cortex CodeDiscovery and static/cloud scanning are read-only and agentless. Proxy, gateway, Shield, and control-plane write tools are separate, explicit runtime or authenticated operations. No secrets leave your machine unless you explicitly enable an outbound integration.
Download counts and popularity will appear here as the collector receives them.
| Version | Published | Direct dependencies | Open version |
|---|---|---|---|
| 0.109.0 | 16 Oct 2026 | 126 |
This describes our collected data; it is not a security assessment.
Observed since 20 Oct, 21:33 UTC
No superseded metadata states collected. Unchanged observations do not create new revisions.
package:d89e3bc201f15e15575c99729e689df63a92a3a28be064bb1e39da8ff6421de4