

 Repository
Current collected state Current
Observed since 20 Oct, 22:18 UTC
No superseded metadata states collected. Unchanged observations do not create new revisions.
Stops your coding agent from pushing unverified work. Your agent does the reviewing; a state machine records the result per-commit and gates the push.


Stop your coding agent from pushing unverified work.
Agentic Preflight checks a coding agent's work before it is pushed. It works with Codex, Claude Code, Cursor, OpenCode, and Amp. It guides the coding agent already working in your repository through review, documentation, lint, and test stages, then records the result against the exact commit. Its pre-push hook blocks the normal push path when that evidence is missing or stale.
Of 408 merged pull requests across four of the author's own repositories from August 3 to September 6, 2026, 323 record an Agentic Preflight run. The dogfooding case study reports what that record shows and what it does not.
You need Git 2.38+, Python 3.11 through 3.13, and
uv. Install the CLI and the
integrations for the coding agents you use:
uv tool install agentic-preflight
agentic-preflight integrations install codex claude cursor opencode amp
Remove the integration names you do not use.
Then initialize each repository you want to protect:
cd your-repo
agentic-preflight init
git add .agentic-preflight.toml
git commit -m "Configure Agentic Preflight"
init writes a commented configuration file and installs an advisory pre-push hook.
Review the generated configuration before starting a run because its setup, lint, test,
and optional command-review entries execute with your user privileges.
Make and commit your product change, then ask your coding agent to invoke
$agentic-preflight in Codex or /agentic-preflight in Claude Code. The installed skill
drives the run, presents any findings, and follows each command returned by the CLI.
If you try to push the changed commit before its run is green, the hook stops the push and tells you how to start or resume verification. After the run passes, the agent shows the target remote, branch, commits, and risk before publication.
The agent pushes only when you asked it to or your standing instructions permit it; see
push and pull-request authorization.
Set [gate] mode = "manual" when only a person should run the final Git command.
The installation guide covers source installs, upgrades, project-scoped skills, other Agent Skills clients, and removal.
Agentic Preflight complements prompts, ordinary Git hooks, hosted CI, and human review. It does not replace them.
Prompt instructions can ask an agent to review its work and run tests, but the resulting conversation is not a record bound to a commit. Traditional hooks run deterministic commands well, while hosted CI validates code after publication. Agentic Preflight joins those checks into an ordered, resumable workflow before push and records what happened against the commit that passed.
That distinction matters when:
Agentic Preflight is advisory by design. It makes missing or stale evidence visible in the
normal workflow, but it is not a security boundary and a person can bypass the local
hook with git push --no-verify.
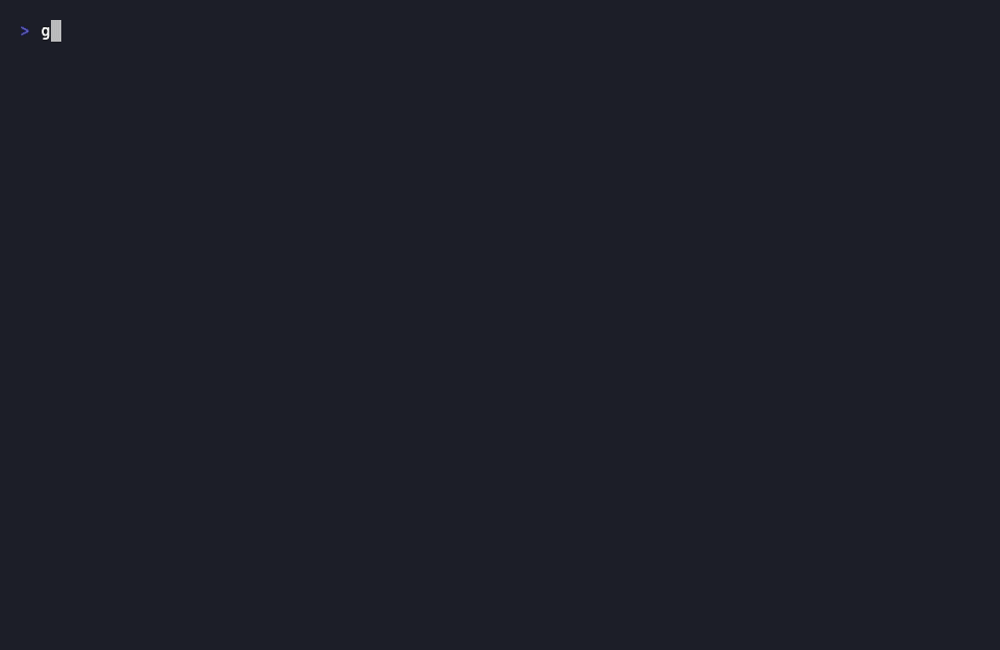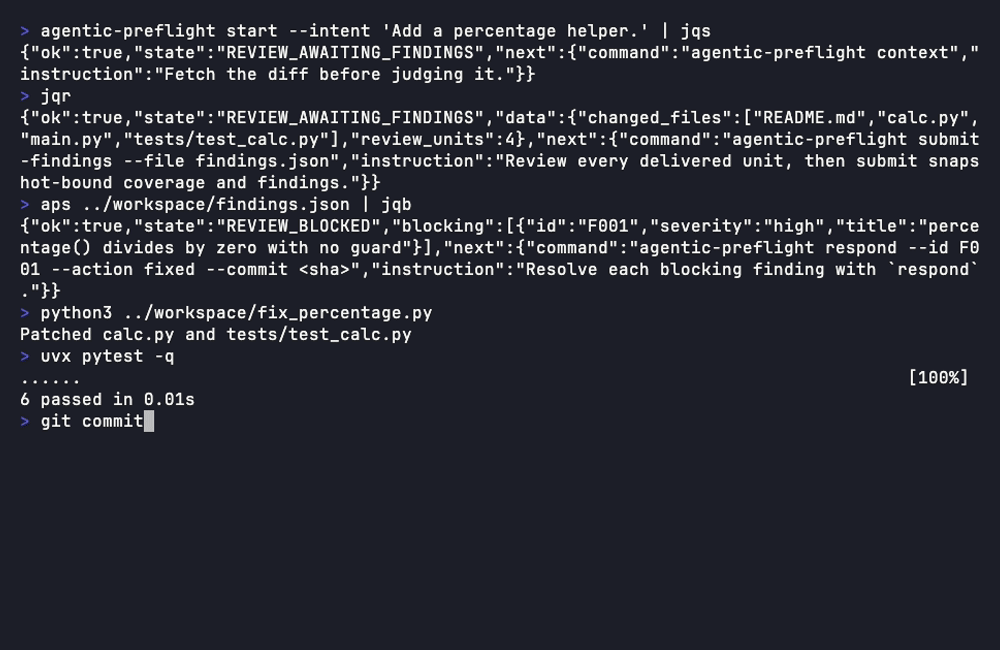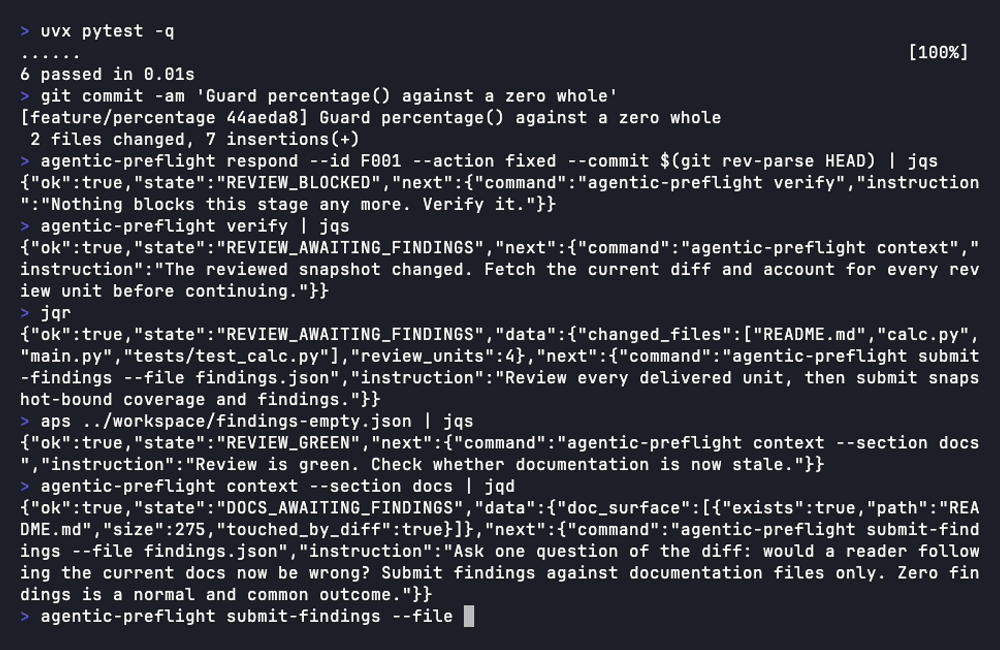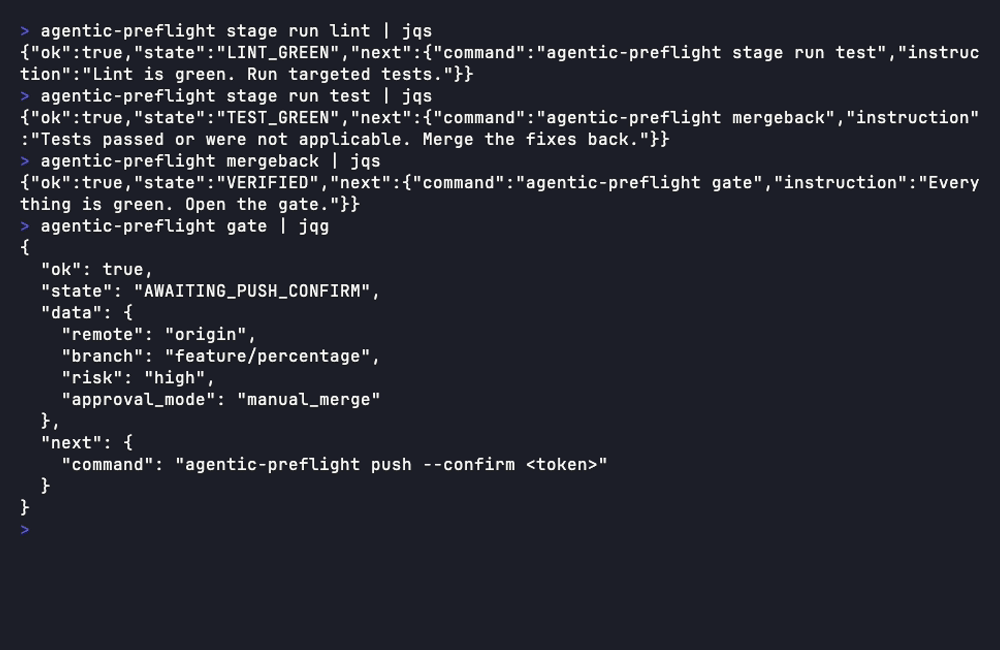
Agentic Preflight moves the change through one ordered workflow:
review -> documentation -> lint -> test -> merge-back -> gate -> push
At the start of a run, the agent supplies your objective and acceptance criteria. When
origin exists, Agentic Preflight fetches it and rebases the validation worktree onto
the fresh base before review, or merges the base in when a rebase would change what the
branch lands. Every agent-facing workflow command returns one JSON
object with the single next legal command, so an interrupted run can resume from
recorded state.
The stages provide different checks:
Equivalent-content rebases can reuse review and documentation evidence when their inputs still match. Applicable lint and test stages run again in every new run, even for identical trees. Keep the producer and protected verifier on the same version; see the fingerprint contract.
Pull-request merge polling and post-merge cleanup are disabled by default. Set
[pr] automated_cleanup = true to opt in.
Run agentic-preflight status in the source worktree to inspect or resume its run. Use
agentic-preflight status --all to inventory runs across linked worktrees.
Commit .agentic-preflight.toml at the repository root. A section in it replaces the
matching section of the user-wide ~/.config/agentic-preflight/config.toml as a whole.
Use it to set:
Unknown keys are errors; retired [ci] and [reuse] sections are ignored with a
warning. Remove those sections and [hook] enabled when upgrading from 0.6.0; see
the 0.7 upgrade guide.
Commit configuration changes before starting the run they
should affect; each run snapshots its resolved configuration. See the
configuration reference
for every option and a complete example.
Warning: A repository can configure setup, lint, test, and independent-review commands that execute with your privileges. Run Agentic Preflight only in repositories whose code and build commands you are willing to execute.
The default in_place mode validates in the current checkout. It suits a clean,
dedicated one-agent/one-PR worktree and can reuse that checkout's installed dependencies.
Set [worktree] mode to reusable or strict when validation should leave the source
checkout untouched. Isolated validation worktrees do not inherit .venv, node_modules, .env,
or other ignored files. Configure setup_command for dependencies and copy_files for
required ignored files. The
worktree-modes guide
explains the tradeoffs, concurrency model, secret handling, and recovery behavior.
A successful merge-back writes a versioned JSON attestation as a Git note on the exact commit. The attestation records review coverage, finding dispositions, stage results, policy, and the inputs that determine whether evidence still applies after a history rewrite.
The local hook checks the commit being pushed. A protected-base GitHub workflow can also
verify the attestation and enforce the configured high-risk approval mode before merge. This
requires forge configuration; committing .agentic-preflight.toml alone does not change
branch protection. See
Portable attestations and CI enforcement
for setup and verification commands.
The user workflow above is backed by design records, executable tests, and published evaluation material. Follow the question you want to investigate:
| Question | Design or evidence |
|---|---|
| How does this workflow compare with its inspiration? | Prior art and differentiation |
| Where does responsibility pass between the coding agent, CLI, and shell commands? | ADR 0001: orchestration boundaries |
| How can linked worktrees run independently and safely? | ADR 0002: worktree-scoped run ownership |
| What repository context reaches review, and how is untrusted content bounded? | Grounded context |
| When can evidence survive a rebase or restack? | Fingerprint contract |
| How are attestations enforced in CI? | CI enforcement |
| What does a second reviewer add, and how are reviewers compared? | Independent review and agreement |
| What public evidence supports the project, and what does it not prove? | Dogfooding case study and public regression eval |
The implementation uses real Git repositories in its integration tests rather than
mocking Git behavior. CI rejects overall test coverage below 85% and installs the built
wheel as a uv tool before invoking the CLI. The
contributor guide
describes the local development workflow.
Agentic Preflight is an advisory pre-push check, not a security boundary.
git push --no-verify.Set [gate] mode = "manual" if the CLI must refuse to perform the final push itself.
Read the limits guide
before relying on attestations or evidence reuse for policy enforcement.
gh when the agent will create pull requests, inspect hosted checks, or verify mergesUse the support guide for help and security-reporting routes. Contributors should start with the contributor guide.
Agentic Preflight is Apache 2.0 licensed. It was created by @elanthus with development contributions from OpenAI Codex and Anthropic Claude.
Download counts and popularity will appear here as the collector receives them.
| Version | Published | Direct dependencies | Open version |
|---|---|---|---|
| 0.7.0 | 14 Oct 2026 | 2 |
This describes our collected data; it is not a security assessment.
Shared repository data · GitHub
Observed since 20 Oct, 22:18 UTC
No superseded metadata states collected. Unchanged observations do not create new revisions.
package:68d2305f09854046a10f6d3a38d4c76bf9be2abedcf1bd74042e57ac30147a74