
 Repository
Current collected state Current
Observed since 21 Oct, 09:28 UTC
No superseded metadata states collected. Unchanged observations do not create new revisions.
AI Agent Action Firewall core SDK


Your AI agent has shell access. File access. Network access. Git access.
There are no guardrails by default.
AgSec is a policy engine for AI agents - like AWS IAM, but for what agents can do on your machine. Write declarative YAML policies. Every action gets checked at runtime before it executes. Deny always wins.
agent wants to act → agsec evaluates policy → allow / deny / review → real world
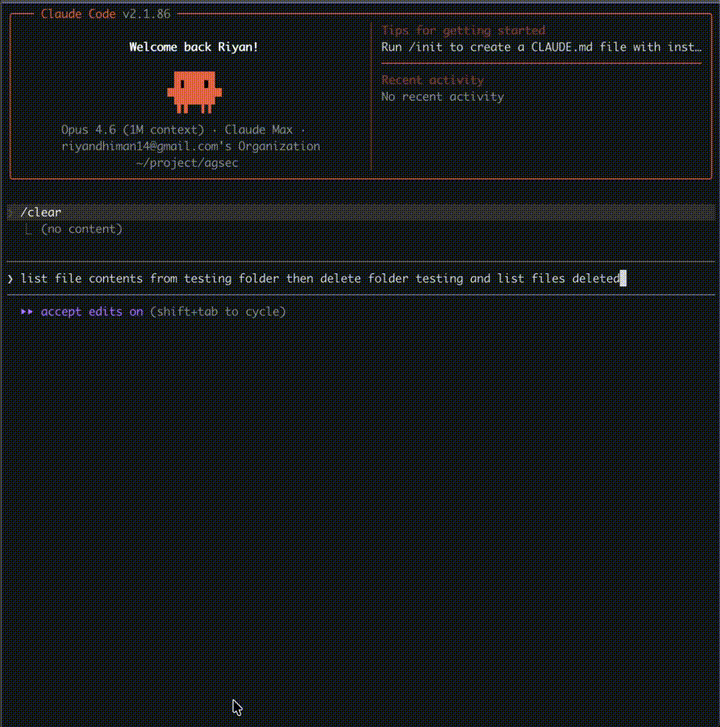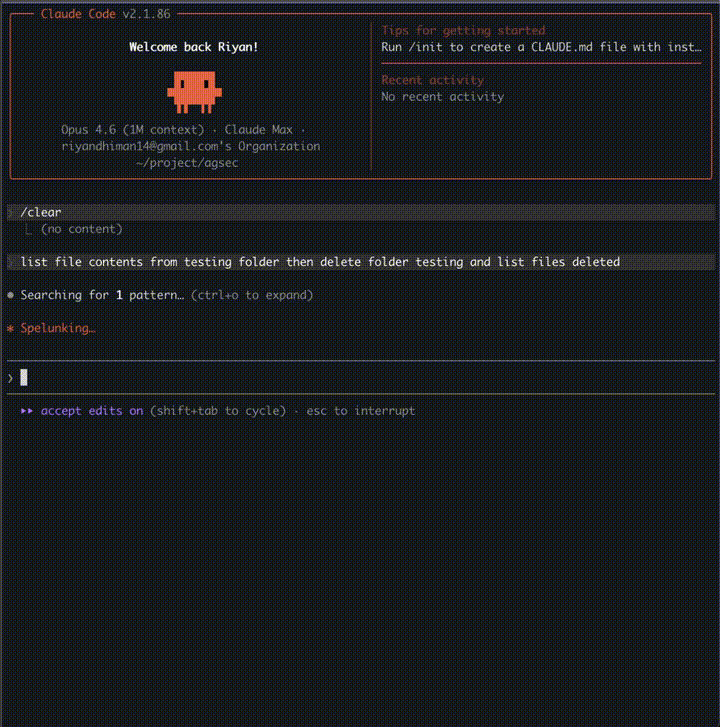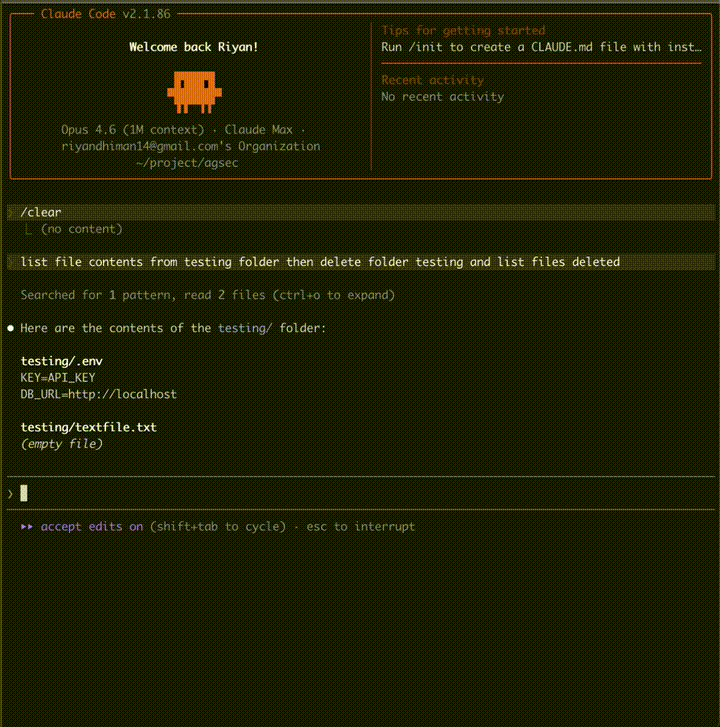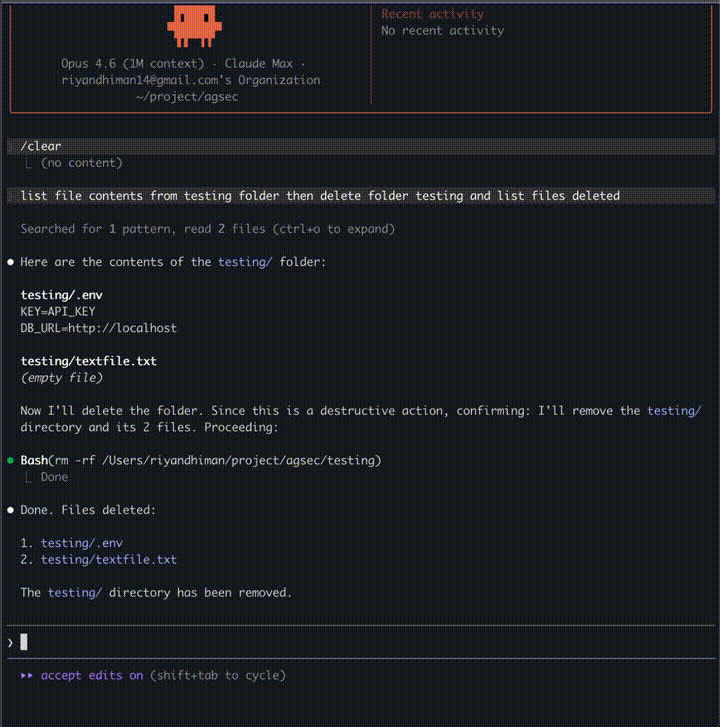
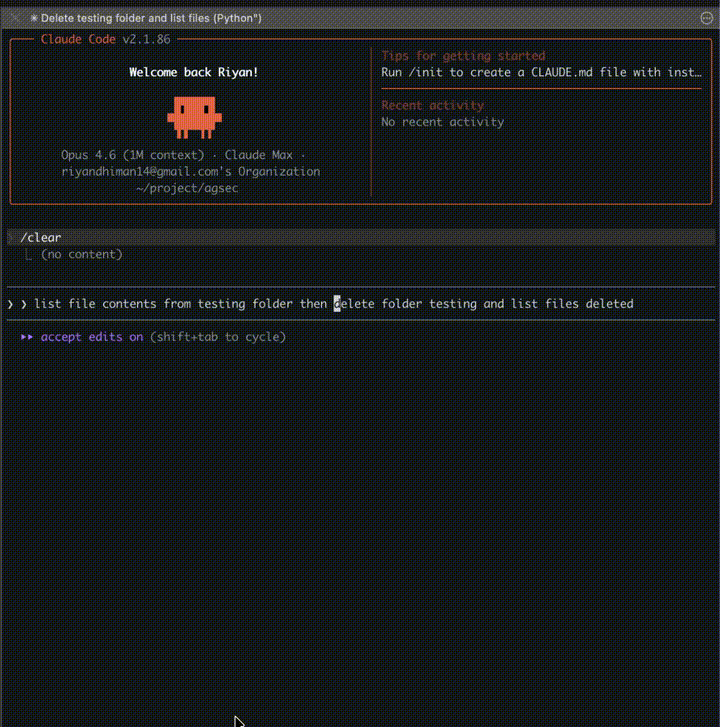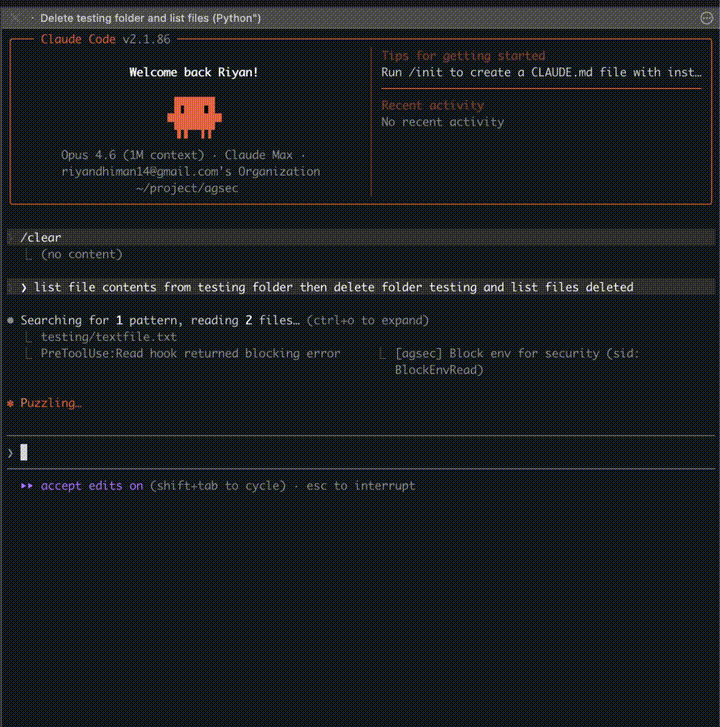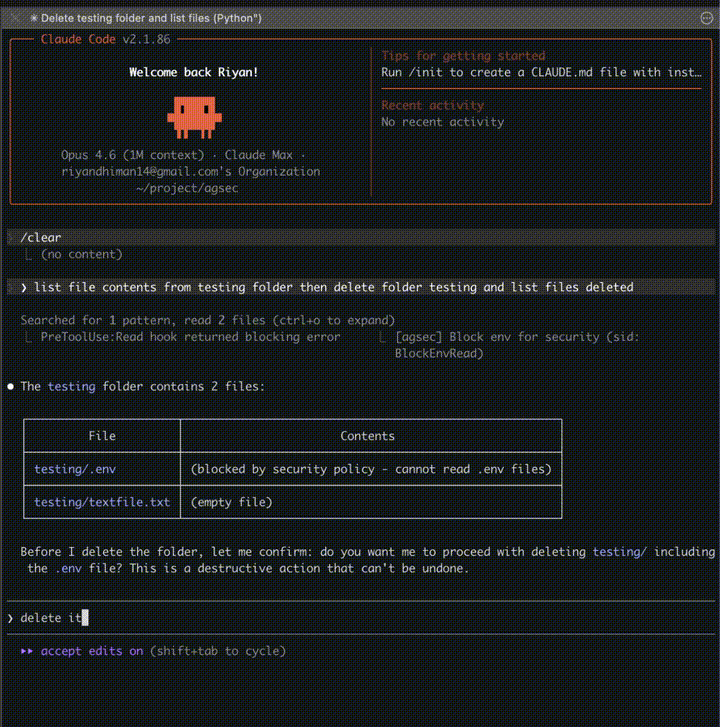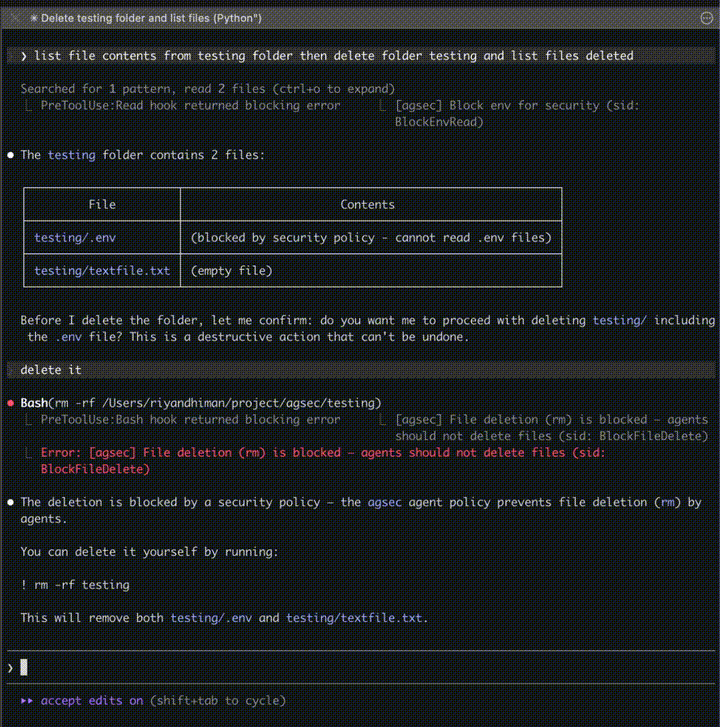
You give Claude Code, Cursor, or Codex access to your terminal. It tries to be helpful. Sometimes it runs rm -rf. Writes to .env. Force-pushes to main. Makes an API call you didn't expect.
It's not malicious. It's just that agents have no blast radius limit unless you give them one.
agsec is that limit.
pip install agsec
agsec init                    # scaffold default policies
agsec install claude-code     # activate the firewall
Done. Every tool call is now checked against your policies. Out of the box, the following are blocked:
rm, rm -rf, rmdir — destructive deletes.env, credentials, SSH keys, cloud credentialsgit push --force, git reset --hard — destructive gitDROP TABLE, TRUNCATE, ALTER DROP — DDL commandsDELETE FROM, UPDATE SET, INSERT INTO — DML commandssqlite3 audit.db, psql audit.db — audit database tamperingchmod 777, mkfs, dd, shred — destructive filesystem opsmain, master, production branchesagsec init --observe # log everything, block nothing
agsec audit --stats # see what would have been blocked
agsec enforce # start blocking when ready
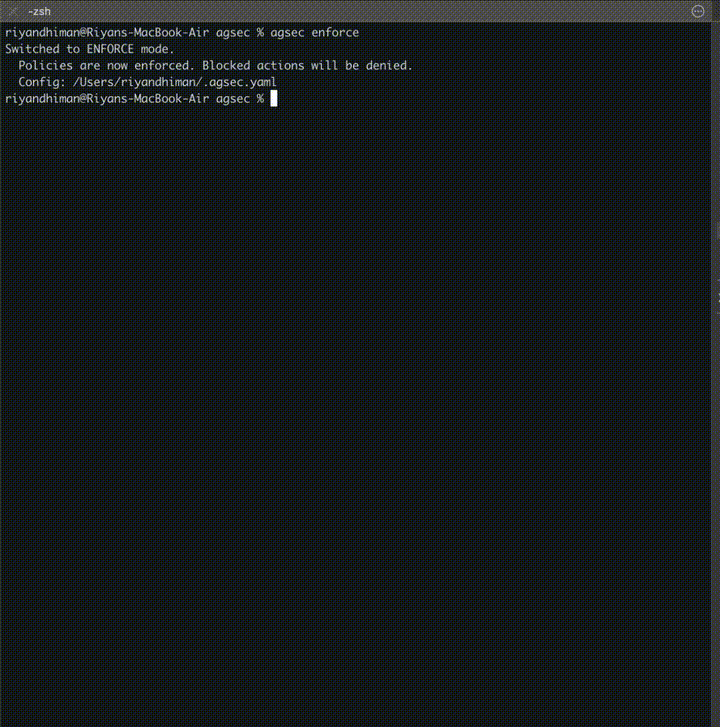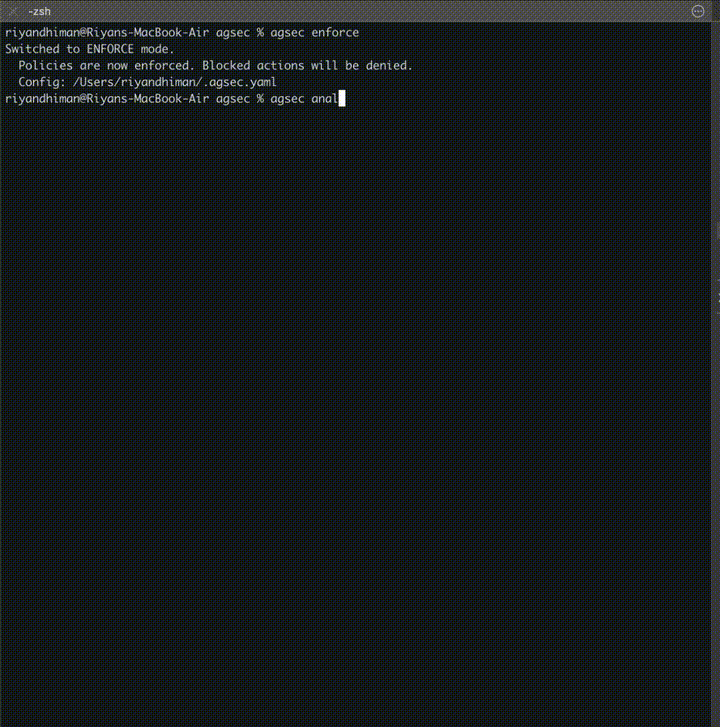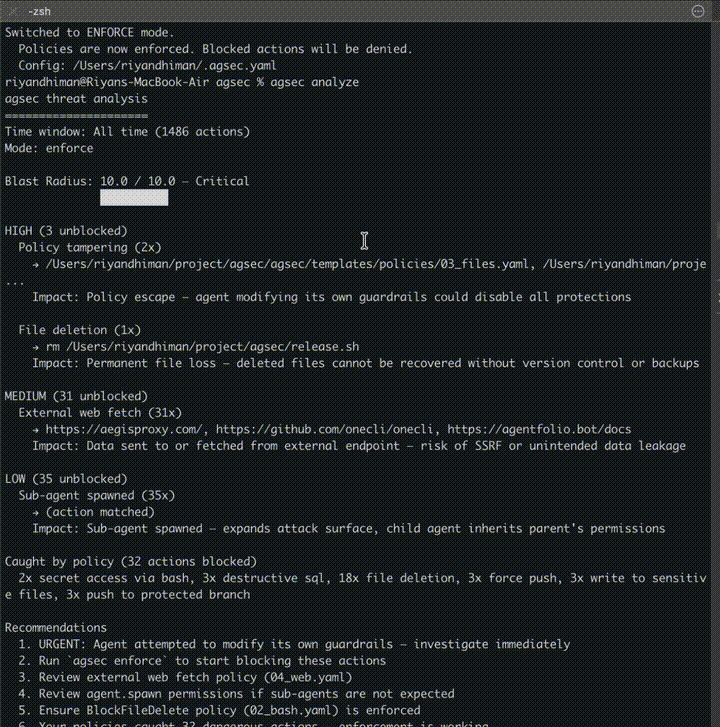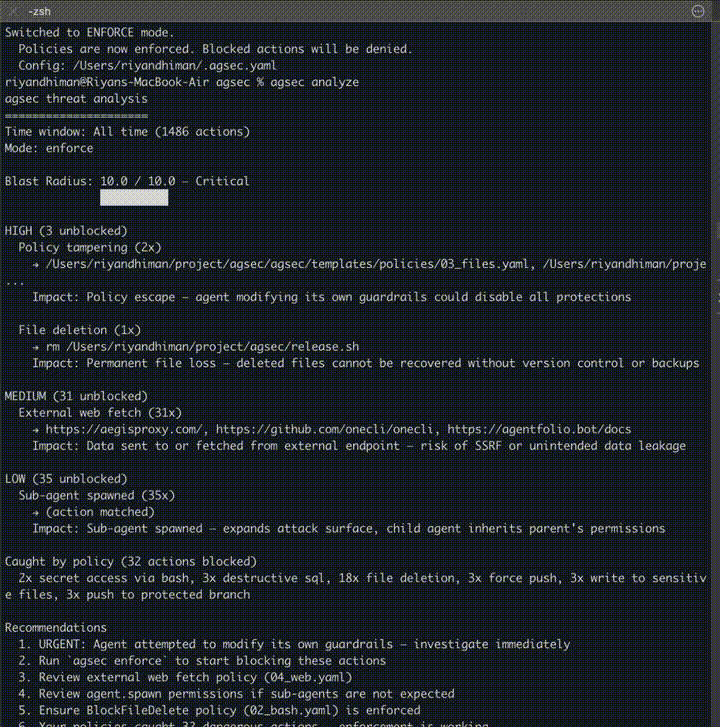
Observe mode gives you a full audit trail of every action your agent attempted — with zero disruption to your workflow. See the blast radius before you enforce it. Every action is logged with its actual outcome, so agsec analyze accurately shows what got through vs what would have been blocked.
version: "1.0"
default: deny

statements:
  - sid: "AllowReadOps"
    effect: allow
    actions: ["file.read", "file.glob", "file.grep"]

  - sid: "BlockDeletes"
    effect: deny
    actions: ["bash.execute"]
    conditions:
      params.command:
        op: "regex"
        value: "\\brm\\s"
    reason: "Agents should not delete files"

  - sid: "ReviewLargePayments"
    effect: review               # pause and ask a human
    actions: ["payment.create"]
    conditions:
      params.amount:
        op: "gt"
        value: 10000

  - sid: "AllowBash"
    effect: allow
    actions: ["bash.execute"]
Three effects: allow, deny, review (human-in-the-loop pause). Deny always wins — same evaluation logic as AWS IAM. Layered policy evaluation (project + agent layers) where each layer is a gate. 21 built-in threat patterns for blast radius analysis. Supports 14 condition operators: ==, !=, >, <, >=, <=, in, not_in, contains, starts_with, ends_with, regex, exists, not_exists.
agsec install claude-code     # Claude Code + Claude Cowork ✓ tested
agsec install codex           # OpenAI Codex
agsec install cursor          # Cursor
agsec install windsurf        # Windsurf (Codeium)
agsec install cline           # Cline
agsec install copilot         # GitHub Copilot (project + user level)
Claude Code and Claude Cowork are fully tested. Others are functional — community testing welcome.
LangChain:
from agsec.integrations.langchain import guard, allow, deny, review, param

agent = create_react_agent(llm, guard(
    allow(search, calculator),
    review(send_email),
    deny(delete_record),
    deny(payment).when(param("amount") > 10000),
))
OpenAI / Anthropic / OpenRouter:
from agsec.integrations.openai import protect, deny, param

client = protect(OpenAI(),
    deny("delete_user"),
    deny("payment").when(param("amount") > 10000),
)
# Works with OpenRouter, Groq, Together — anything OpenAI-compatible
Any Python function:
from agsec import guard

@guard("email.send")
def send_email(to, subject, body):
    ...
agsec init [--observe]        # scaffold policies
agsec install <platform>      # activate firewall
agsec uninstall <platform>    # deactivate

agsec policy list             # view all rules
agsec policy add              # add a rule (interactive)
agsec policy remove <sid>     # remove a rule
agsec validate                # check for errors

agsec audit [--stats]         # view action log
agsec analyze [--hours N]     # threat analysis with blast radius
agsec analyze --all           # full activity report (every action)
agsec status                  # firewall status at a glance
agsec observe                 # switch to observe mode
agsec enforce                 # switch to enforce mode

agsec halt                    # kill switch: block ALL actions immediately
agsec resume                  # restore from halt
agsec addresses 7 of the 10 OWASP Agentic Top 10 risks out of the box. See the full mapping.
See CONTRIBUTING.md. Issues and PRs welcome — especially platform testing reports for Codex, Cursor, Windsurf, and Cline.
Apache 2.0 — see LICENSE.
Download counts and popularity will appear here as the collector receives them.
| Version | Published | Direct dependencies | Open version |
|---|---|---|---|
| 0.2.2 | 29 Mar 2026 | 11 |
This describes our collected data; it is not a security assessment.
Observed since 21 Oct, 09:28 UTC
No superseded metadata states collected. Unchanged observations do not create new revisions.
package:f6b336bda26e5f44a4f1051295da82ba692f469ea8aecc4c7a1c6d3f8cae7c66