

 Repository
Current collected state Current
Observed since 21 Oct, 09:50 UTC
No superseded metadata states collected. Unchanged observations do not create new revisions.
Offline AI agent bill of materials and attack surface scanner


AgentBOM is a local-first pre-commit security guard for AI-agent repositories.
AI-agent repos often mix prompts, tool permissions, MCP config, and API keys. AgentBOM gives you a local commit-time check before risky changes enter git.
agentbom activate.pip install ai-agentbom
cd my-agent-repo
agentbom activate
git commit
Passing commit:
AgentBOM OK
No policy violations found.
Blocked commit:
AgentBOM blocked this commit

CRITICAL Possible OpenAI API key value
.env:1
Value redacted. Remove the key and rotate it.
Secret values are redacted in output.
agentbom activate creates or reuses agentbom.toml and installs a repo-local
pre-commit guard. The default mode is confirm: passing commits print
AgentBOM OK, and AgentBOM asks before committing when policy violations are
found. Activation only affects this local clone and does not overwrite an
existing agentbom.toml unless --force is passed.
agentbom status
agentbom scan . --policy agentbom.toml --html --open
Activation presets:
safe: default, good for normal use.audit: observe without blocking.strict: stronger policy for sensitive repos.agentbom activate --strict remains available as an alias for
agentbom activate --preset strict.
Policy review is advisory by default:
agentbom scan . --policy agentbom.toml --pretty
Make policy violations fail a scan only when you opt in:
agentbom scan . --policy agentbom.toml --enforce-policy
The HTML report includes a Policy Workbench for generating and refining
agentbom.toml from detected providers, models, frameworks, reachable
capabilities, MCP servers, secret references, and policy gaps.
See policy docs for policy format, rollout, local guard modes, and bypass behavior.
Install a repo-local pre-commit guard:
agentbom activate
Modes:
advisory allows commits and warns on policy violations.confirm asks before committing when violations exist.enforce blocks commits when violations exist.The hook is local to the current repository under .git/hooks/pre-commit.
Disable it with:
agentbom deactivate
Troubleshooting prompt or PATH issues: troubleshooting.
| Area | Examples |
|---|---|
| Providers and models | OpenAI, Anthropic, Gemini, Ollama, OpenRouter, GPT/o-series, Claude, Gemini, Llama, Mistral, Qwen, Grok, Cohere, Perplexity |
| Frameworks | LangChain, LangGraph, LlamaIndex, CrewAI, AutoGen/AG2, Semantic Kernel, Pydantic AI, OpenAI Agents SDK, Mastra, Vercel AI SDK, LiteLLM |
| Prompts | AGENTS.md, CLAUDE.md, prompts/*.md, prompt YAML |
| MCP | mcp.json, .mcp.json, claude_desktop_config.json, Cursor/Claude MCP config paths |
| Capabilities | shell, code execution, network, database, cloud, MCP tool invocation |
| Secret references | credential names such as OPENAI_API_KEY, never values |
| Secret leak findings | likely AI/API credential values, always redacted |
| Policy gaps | prompt files, MCP config, shell/cloud access without policy documentation |
Findings include source paths, confidence, reviewer-facing rationale, and mitigation signals where static evidence is available.
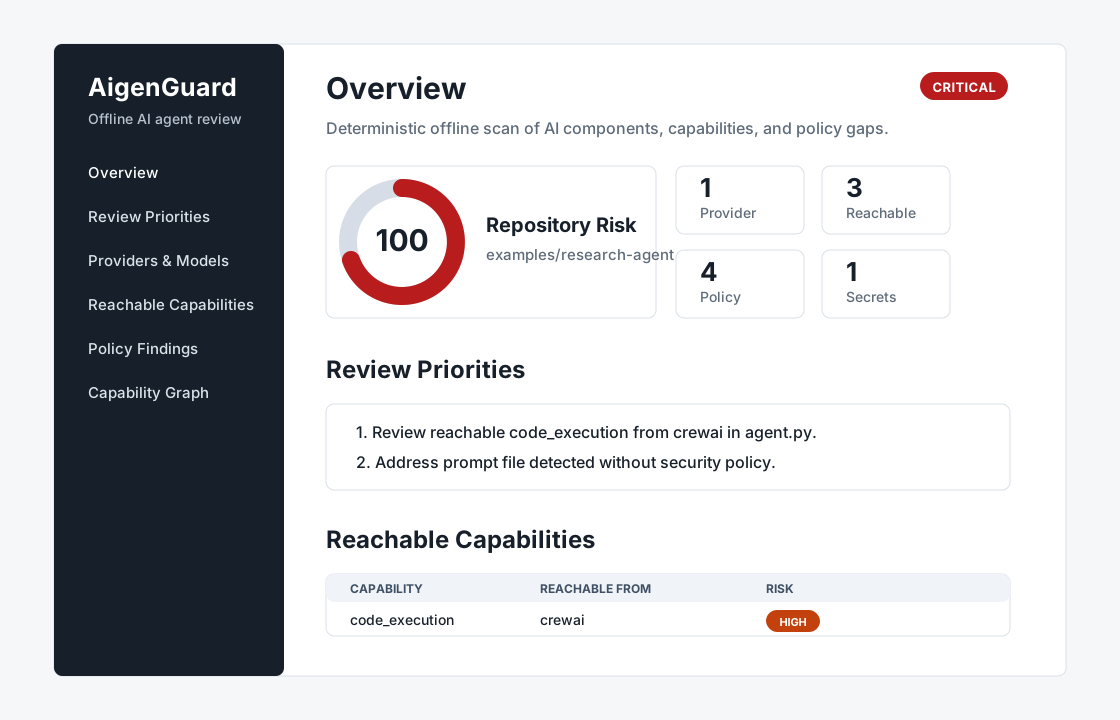
Generate review artifacts:
agentbom scan . --output-dir agentbom-report --html --mermaid --sarif --pretty
Diff-aware scans compare the current report with a baseline JSON report:
agentbom scan . --baseline agentbom-baseline.json --fail-on-new high --sarif --html --pretty
--fail-on-new accepts low, medium, high, or critical.
See the report guide for field definitions and reviewer workflow.
Use the action in pull requests to publish reports and a workflow job summary.
name: AgentBOM

on:
  pull_request:
  push:
    branches: [main]

permissions:
  contents: read

jobs:
  scan:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4

      - name: Run AgentBOM
        uses: vlcak27/agentbom@v0.8.0
        with:
          path: .
          fail-on: none
          sarif-upload: false
          html: true
          output-dir: agentbom-report

      - name: Upload AgentBOM reports
        uses: actions/upload-artifact@v4
        with:
          name: agentbom-report
          path: agentbom-report/
Enable SARIF upload only when you want GitHub code scanning alerts:
permissions:
  contents: read
  security-events: write
More details: GitHub Action docs.
pip install -e ".[dev]"
ruff check .
pytest
Or run the project check:
make check
Useful docs:
Download counts and popularity will appear here as the collector receives them.
| Version | Published | Direct dependencies | Open version |
|---|---|---|---|
| 0.8.0 | 20 May 2026 | 4 |
This describes our collected data; it is not a security assessment.
Observed since 21 Oct, 09:50 UTC
No superseded metadata states collected. Unchanged observations do not create new revisions.
package:d54183a735a54194ba171bdeb1d347ba7eee2e12ccc6ec21fa8410dfd222fda0